




This comparison covers ten tools and splits them on exactly that line. Some monitor the outside world, and some manage controls and evidence inside the organisation.
One connects the two, carrying a change through to a redrafted, approved document.
Every entry draws on factual G2 and Capterra reviews and a detailed analysis of each tool in October 2026.
Key Takeaways (TL;DR)
What Regulatory Compliance Monitoring Software Does: Tracks changes from regulators, legislatures and official publishers, assesses what each change affects, assigns the work to someone, and records that it was done.
Why Most Teams Are Unhappy With Theirs: The two halves of the job sit in different products. Regulatory intelligence tools watch the outside world and have no view of your documents, while GRC platforms manage controls and evidence but do not monitor regulation. Teams bridge the gap manually.
Best Overall Regulatory Compliance Software: LEGALFLY. Legal Radar covers 130+ jurisdictions and tests each change against your own contracts and policies, with the redraft and approval workflow running in the same system.
What Sets LEGALFLY Apart: Whole legal workflows run end to end from a detected regulatory change through to a redrafted document and legal sign-off, on documents that are anonymised before analysis begins, on an architecture designed before the current generation of models existed.
How to Choose: Work out whether your gap is monitoring, impact analysis or evidence, check the tool covers the jurisdictions you actually operate in, and ask what happens to a change after the alert lands.
To find out how LEGALFLY could work for you, schedule a call with one of our experts.
Best Regulatory Compliance Software in 2026 at a Glance
Tool | Best For | Key Features | Pros | Cons |
LEGALFLY | In-house legal and compliance teams needing change monitoring connected to their own documents | End-to-end agentic workflows through Agent Studio, anonymisation before analysis, Contract Intelligence across the lifecycle, Legal Radar across 130+ jurisdictions, playbook-driven review | Carries a detected change through to a redrafted document and approval; anonymisation applied at import; impact tested against your own contracts and policies | Sales-led evaluation, so the first step is a scoped demo rather than a self-serve trial |
Optro (formerly AuditBoard) | Internal audit and SOX teams running compliance alongside a formal audit programme | Audit management, compliance tracking, controls testing, risk linkage, issue management, reporting | Centralised audit and compliance in one place, with responsive support during implementation | Reviewers report frequent bugs and update disruptions, and a learning curve on advanced functions |
LogicGate Risk Cloud | Teams wanting to build compliance workflows to their own process without writing code | No-code workflow builder, risk register, controls mapping, third-party risk, reporting dashboards | Configurable to almost any process, with consolidation of separate GRC workstreams into one app | Reviewers describe a steep learning curve, a confusing build environment and reporting that needs extra configuration |
Hyperproof | Compliance operations teams managing multiple frameworks and continuous evidence collection | Control framework management, evidence automation, audit readiness, compliance tracking, integrations | Automated evidence collection across multiple frameworks, with audit readiness built into the workflow | Reviewers cite report customisation difficulty, a setup process they describe as unintuitive, and limited reporting flexibility |
Diligent One Platform (formerly HighBond) | Enterprises reporting risk and compliance upwards to boards and audit committees | Audit management, risk assessment, controls monitoring, data analytics, board reporting | Breadth across audit, risk and compliance with interconnected modules and board-level reporting | Reviewers report limited flexibility in some modules, occasional bugs and limited configurability |
NAVEX One | Organisations running policy management and ethics alongside compliance obligations | Policy management, whistleblowing and ethics reporting, third-party risk, compliance training, incident management | Policy distribution and attestation at scale, with ethics and compliance in one place | Reviewers raise an unintuitive interface, slow support responses and a steep learning curve |
Thomson Reuters Regulatory Intelligence | Large financial institutions needing broad regulatory content with analyst commentary | Global regulatory change feeds, expert analysis, obligation libraries, alerting, reporting | Editorial depth and interpretation that few competitors attempt | Built around financial services, and impact mapping to your own documents stays manual |
Wolters Kluwer OneSumX Regulatory Change Management | Banks and insurers mapping regulatory change to an internal controls library | Curated regulatory content, obligation mapping, control linkage, assessment workflow, audit reporting | Controls mapping that turns monitoring into auditable governance | Requires an existing controls library, and financial services taxonomies limit the fit elsewhere |
LexisNexis Regulatory Compliance | Operational businesses managing obligations tied to specific business activities | Obligation registers, jurisdiction-specific content, change alerts, activity mapping, ownership tracking | Obligation-level granularity that operational teams can act on directly | Coverage depth varies by jurisdiction, and registers need configuring against your activities first |
Regology | Teams wanting AI-led regulatory discovery and an obligation library in a lighter system | AI regulatory discovery, law library, obligation mapping, alerting, task assignment | Lighter implementation than enterprise GRC suites, with discovery for establishing your footprint | Enterprise governance features are thinner, and content maintenance should be tested on jurisdictions you know well |
Why Teams Need Regulatory Compliance Monitoring Software
Regulatory change moves fast and manual monitoring does not scale. One person can realistically follow one or two jurisdictions properly, and most regulated businesses now operate across considerably more.
The EU AI Act, DORA, NIS2, CSRD and CSDDD arrived close together, each with deadlines and each touching different documents. Teams that were coping two years ago are not coping now.
What Regulatory Compliance Monitoring Software Does
The category covers four jobs that rarely sit in one product. Monitoring watches official sources for changes, and impact analysis works out what each change affects.
Remediation then updates the affected documents, and evidence records that all of it happened.
Most tools do one or two of these well. Regulatory intelligence products are strong on monitoring and weak on everything after it. GRC platforms are strong on evidence and controls and do no monitoring at all.
That split is why so many compliance functions run two systems and a spreadsheet between them.
Where Most Compliance Tools Fall Short
The gap opens at impact analysis, and it is the expensive one. A feed tells you a rule published. Your business then asks which of our contracts, policies and processes conflict with it now.
Answering that means reading your own documents against the new requirement. Most regulatory intelligence products have no view of your paper at all, so the mapping returns to your team every time.
GRC platforms have the opposite problem. They know your controls and your evidence, but nothing arrives to tell them a rule changed, so someone has to enter it by hand.
The result is familiar. A well-run feed produces accurate alerts, a compliance team spends its week working out which ones matter, and a legal team redrafts whatever they find.
Best Software for Regulatory Compliance Overall

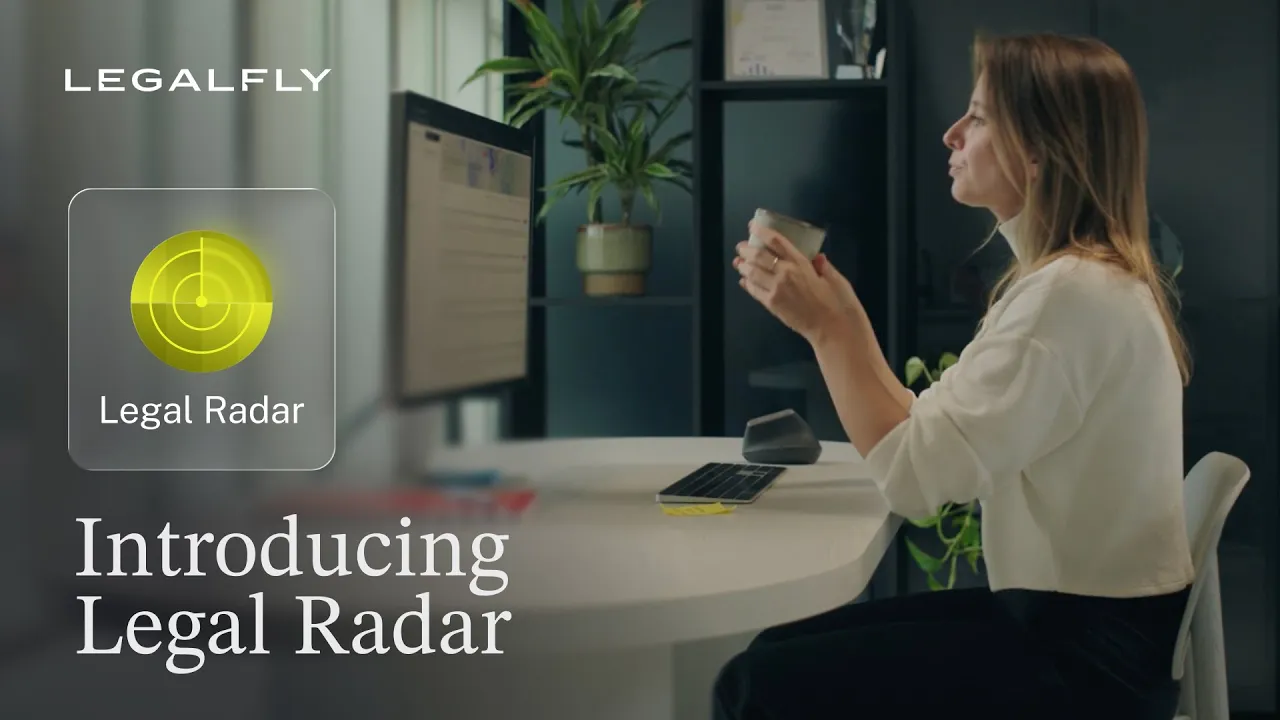
LEGALFLY is the best software for regulatory compliance monitoring because it closes the gap rather than sitting on one side of it. Legal Radar monitors 130+ jurisdictions, delivers plain-English summaries with business impact and recommended next steps, and tests each change against the customer's own contracts and policies.
From there the workflow keeps running. A high-impact change identifies the affected documents in SharePoint, Google Drive or LEGALFLY, redrafts them, routes the redraft for legal review and uploads the approved version, with an audit trail across every step.
Best Regulatory Compliance Software: In-Depth Review & Comparison
The ten tools below fall into three groups. There are legal operating systems where monitoring connects to the documents it affects, GRC platforms built around controls and evidence, and regulatory intelligence suites built around content and analysis.
Each entry covers what the product does, who it fits, its strongest capabilities, why it belongs on this list, what reviewers say, and where it stops.
1. LEGALFLY

Overview
LEGALFLY is the legal operating system for corporates. It gives in-house teams AI-native workflows for intake, contract review, drafting, due diligence and legal research, with security and anonymisation underneath all of it.
Legal Radar is the regulatory monitoring capability inside that system, and its position is what makes it different. Because monitoring sits alongside contract review, drafting and document handling, a regulatory change can become a redrafted clause without leaving the system or opening a ticket.
Customers include SAP, Lufthansa, Bosch and KPMG, and the European Commission's HR Directorate-General, alongside many others across banking, insurance, technology and manufacturing.
To find out how LEGALFLY could work for you, schedule a call with one of our experts.
Ideal For
In-house legal and compliance teams of 3 to 200 people supporting enterprises of 200 to 100,000 employees
Multi-jurisdiction organisations facing the EU AI Act, DORA, NIS2, CSRD and CSDDD across several regions at once
Compliance functions that have to prove they acted, not only that they knew
Banking, insurance, technology, manufacturing and transport businesses where the security review decides the shortlist
Teams whose compliance work stalls at the point where a change has to become a redrafted document
Top Features
Agent Studio for end-to-end legal workflow automation. A detected regulatory change triggers a workflow that identifies affected documents in SharePoint, Google Drive or LEGALFLY, redrafts them, routes the redraft for legal review and uploads the approved version, with conditional logic and escalation thresholds throughout.
Anonymisation before analysis. Names, roles, company details and identifiers are pseudonymised at import, with context and structure intact, so identifiable data never reaches a third-party model. This is applied by default rather than configured per workflow.
Contract Intelligence across the full lifecycle, from drafting and negotiation through approval and e-signature to renewals, expirations, notice periods, obligations and key dates.
Playbook-driven ai contract review with playbooks configured for new rules, so existing agreements can be checked against a regulation that did not exist when they were signed. 120+ lawyer-built playbooks across 100+ document types, plus a builder that generates a custom playbook from your own golden contracts in around two minutes.
Multi Review for bulk analysis across entire data rooms, applying one playbook to hundreds of documents at once, which is how a portfolio gets checked against a new requirement inside a deadline.
Legal Radar, regulatory tracking software monitoring official regulators and publishers across 130+ jurisdictions, 24/7. Source types include Official Gazettes, Supervisory Authorities, National Banks, Regulatory Authorities, Official Legal Databases, Courts, Councils and Non-Profits, with in-product categories for Banking and Finance, Data Protection and Privacy, Tax and Structuring, Cyber Security, and AI and Technology.
Discovery, ai for legal research grounded in 1000+ official legal sources across 130+ jurisdictions, with citations and auditable reasoning on every answer, plus Drafting for AI contract drafting that produces the updated document.
Integrations with Microsoft Word, SharePoint, Outlook, Teams, Google Drive, Slack, NetDocuments and Microsoft Copilot, each carrying automatic anonymisation.
Why We're the Best Regulatory Compliance Software
The honest version of this argument starts with what we are not competing on. The GRC platforms on this list have spent years building controls libraries, evidence automation and audit reporting, and a team whose job is SOX testing or ISO certification evidence has better options here than us.
We compete on the step between knowing and acting. A change detected by Legal Radar is tested against your own contracts and policies, the affected documents are identified across your repositories, and the redraft and approval run in the same system.
That is a workflow rather than a notification, and it is the part most teams currently do by hand.
Scope is the second argument. Legal Radar sits alongside contract review, drafting, research and document handling, so one purchase answers the regulatory question and the contract backlog rather than adding another single-purpose tool to the stack.
Anonymisation is the third. Documents are anonymised before analysis begins, which is what clears the security reviews that stop other AI tools in regulated environments.
Pros
Turns updates into decisions: impact is tested against your own contracts and policies, what needs updating is flagged, and the redraft and approval run end to end in the same system.
Impact you can act on: every update carries a plain-English summary, the business impact and the recommended next steps, so the output tells you what to do rather than only what changed.
High-signal alerts across 130+ jurisdictions: new and upcoming rules are tracked 24/7 from official regulators and publishers, and you choose the jurisdictions, topics and frameworks that matter.
Every alert is defensible: source links, rationale and ownership sit on each alert, with an audit trail across every compliance action, and documents are anonymised before analysis begins.
One system beyond compliance monitoring: the same place that tracks regulatory change also handles contract review and drafting, due diligence across entire data rooms, and the workflows that connect them.
Cons
Sales-led evaluation, so the first step is a scoped demo and a discovery conversation rather than a self-serve trial
Focused on tracking regulatory change and mapping its impact to your own contracts and policies, rather than on controls testing, evidence collection and audit programme management
Built for in-house legal and compliance teams rather than as a standalone regulatory data feed for a financial services risk function
Customer Reviews
LEGALFLY holds 4.7 out of 5 across eight Capterra reviews, with value for money rated 4.8, customer service 4.7 and features 4.4. Reviewers describe faster document review and legal research, with a general counsel in hospitality and several practising lawyers describing it as part of their daily work.
What users highlight most is speed on document-heavy work and the ability to get reliable answers on specific jurisdictions. One reviewer describes it as an all-round booster across the legal workload rather than a single-task tool.

Final Verdict
If your compliance work stalls at the point where a change has to become a redrafted contract or policy, this is the strongest option here. Monitoring, impact testing, redrafting and approval sit in one system, and the same system handles the contract review workload underneath.
If what you need is controls testing, evidence collection and audit programme management, the GRC platforms further down this list were built for exactly that and we would say so in the demo.
To find out how LEGALFLY could work for you, schedule a call with one of our experts.
2. Optro (formerly AuditBoard)

Overview
Optro is a connected risk suite built around internal audit, SOX compliance and risk management. Audit programmes, control testing, issue tracking and compliance obligations sit in one system, so the evidence gathered for one requirement can be reused against another rather than collected twice.
The product was built for the internal audit function first, and that heritage shows in how it is organised. Workpapers, testing cycles and issue remediation are first-class objects, and compliance obligations hang off the same controls structure.
Reviewers are predominantly in finance, accounting and internal audit, with financial services, banking and insurance the heaviest industries. That tells you who the product was designed for more clearly than any feature list.
Ideal For
Internal audit functions running SOX or equivalent control testing programmes
Compliance teams that sit alongside audit and share a controls library
Financial services, banking and insurance organisations with formal assurance structures
Enterprises consolidating audit, risk and compliance workpapers into one system
Teams needing repeatable testing cycles with documented evidence behind each control
Top Features
Audit management covering planning, workpapers, testing cycles and issue tracking
Controls library shared across audit, risk and compliance requirements
Risk assessment and linkage between risks, controls and obligations
Automated workflow for assigning, reviewing and signing off testing work
Reporting and dashboards for audit committees and executive stakeholders
Integrations including Microsoft 365, Excel, Power BI, Teams, Alteryx and Azure Portal
Why It's a Strong Regulatory Compliance Option
Optro is one of the strongest choices where compliance is governed by the assurance function rather than by legal. If your obligations are already expressed as controls with owners and testing schedules, the product slots into an operating model you have rather than asking you to build a new one.
The reuse argument is the second one. Reviewers consistently describe collecting evidence once and applying it across multiple frameworks and audits, which is where most of the manual duplication in a compliance programme sits.
Scale is the third. With more reviews than anything else in this comparison and deployment across a large share of the Fortune 500, the product has been through the kind of enterprise rollouts that surface problems early.
Pros
Audit, risk and compliance in one connected system rather than three
Evidence collected once and reused across frameworks and testing cycles
Workflow automation for assignment, review and sign-off on control testing
Reporting built for audit committees and executive stakeholders
Integrations across the Microsoft estate plus analytics tools such as Power BI and Alteryx
Cons
Reviewers report bugs and update-related disruption affecting workflow
Advanced functions carry a learning curve, with reviewers describing parts of the interface as unintuitive
Customisation is limited in places relative to the no-code builders in this comparison
Built around audit and controls rather than regulatory change monitoring, so changes have to be entered rather than detected
Four months to implement with fifteen months to return
Customer Reviews
Optro holds 4.6 out of 5 across 1,625 G2 reviews and 4.7 out of 5 across 415 Capterra reviews, the largest evidence base in this comparison. Reviewers praise the centralisation of audit documentation, the ease of linking risks to controls, and automated approvals that remove chasing from the testing cycle. Customer support draws consistent positive comment, particularly during implementation.
The criticisms are specific enough to plan around. Capterra's own summary of the review base names frequent bugs and update disruptions, with reviewers describing functionality breaking after releases. Several reviewers also describe parts of the interface as unintuitive and note limits on customisation when the process does not match the product's assumptions.

Final Verdict
Optro is recommended for organisations where internal audit owns or co-owns compliance, and where obligations are already managed as controls with testing schedules behind them. On evidence reuse and audit programme management it is difficult to beat.
It is a weaker fit for in-house legal teams whose problem is regulatory change itself. The product manages what you already know you have to do, and nothing in it watches regulators to tell you the requirement moved.
3. LogicGate Risk Cloud

Overview
LogicGate Risk Cloud takes a different approach from most of this category. Rather than shipping fixed compliance modules, it provides a no-code builder that teams use to construct their own applications: a compliance register here, a third-party risk workflow there, an issue management process alongside both.
That design answers a real problem. Compliance processes differ enormously between organisations, and a product built around one company's assumptions tends to need working around at another.
The trade-off is that someone has to do the building. Reviewers describe the flexibility as the main reason they chose it and the learning curve as the main reason it took time to get value.
Ideal For
Teams whose compliance processes do not match a standard template
Organisations consolidating several GRC workstreams into one system
Compliance functions with internal capacity to build and maintain applications
Businesses with existing GRC experience who know what they want to construct
Enterprises wanting risk, compliance and third-party management in one environment
Top Features
No-code workflow builder for constructing compliance applications to your own process
Risk register with linkage between risks, controls and obligations
Third-party and vendor risk management workflows
Issue and remediation tracking with assignment and escalation
Reporting dashboards across risk and compliance data
Integrations into evidence sources including Jira, Asana and other operational systems
Why It's a Strong Regulatory Compliance Option
LogicGate is one of the smartest choices where the compliance process is genuinely unusual. Reviewers describe eliminating manual spreadsheet-based tracking and consolidating audit, risk and compliance into one application, which is the consolidation case made concrete.
Configurability without code is the second argument. A compliance manager can build and adjust a workflow without raising a development ticket, which matters when regulatory requirements change faster than an IT backlog moves.
The automation layer is the third. Reviewers describe the workflow automation as helping small teams work smarter rather than harder, which is the realistic outcome for a compliance function that cannot hire its way out of the problem.
Pros
No-code builder that adapts to almost any compliance process
Consolidates risk, compliance, audit and third-party workstreams into one application
Workflow automation that reduces manual tracking and chasing
Strong training resources, which reviewers repeatedly credit for getting teams productive
Customer support draws consistent praise, including from reviewers who are critical elsewhere
Cons
Reviewers describe a steep learning curve and a build environment they find confusing
Advanced reporting needs extra configuration, with some reviewers reaching for third-party tools
Initial setup is challenging without prior governance, risk and compliance experience
Workflow creation is described by several reviewers as not always intuitive
No regulatory monitoring, so changes have to arrive from somewhere else
Customer Reviews
LogicGate holds 4.6 out of 5 across 191 G2 reviews and 4.7 out of 5 across 65 Capterra reviews. Reviewers consistently praise the customisability and ease of use once configured, describing the elimination of manual spreadsheet tracking and the ability to tailor workflows to specific business needs. Training resources and technical support are singled out repeatedly as reasons the implementation succeeded.
The criticisms cluster around the build experience. Reviewers describe the platform as complex and overwhelming at first, with a confusing build environment and time-consuming setup. Reporting is the other recurring theme, with several asking for stronger built-in capabilities and more granular permissions rather than extra configuration work.

Final Verdict
LogicGate is recommended for organisations with non-standard compliance processes and the internal capacity to build and maintain applications. In that setting the flexibility is difficult to match.
It is a poor fit for teams that want a working compliance process in weeks with minimal administration. The learning curve reviewers describe is real, and a team without governance, risk and compliance experience will spend its first months building what more opinionated products ship with.
4. Hyperproof

Overview
Hyperproof is built around compliance operations, with a particular focus on the evidence problem. Organisations certifying against several frameworks at once collect largely overlapping evidence for each, and Hyperproof maps controls across frameworks so a single piece of evidence satisfies every requirement it touches.
Automation handles much of the collection. Integrations pull evidence directly from the systems where it already lives, rather than asking an engineer to screenshot a configuration screen once a quarter.
The buyer skews towards IT and security rather than legal, with information technology, accounting and financial services the heaviest industries in its review base. That shapes both its strengths and its limits for a legal audience.
Ideal For
Compliance teams managing several frameworks simultaneously
Security and IT functions handling SOC 2, ISO 27001 and similar certifications
Organisations wanting continuous evidence collection rather than quarterly scrambles
Teams preparing for recurring external audits with documented trails
Businesses with technical systems that can be integrated as evidence sources
Top Features
Control framework management with cross-mapping between overlapping requirements
Automated evidence collection from connected systems
Audit readiness tracking with gaps surfaced before the auditor arrives
Task management and assignment across compliance programmes
Reporting dashboards on compliance posture
Integrations including AWS Lambda, GitHub, Jira, Microsoft SharePoint, Google Workspace, Coupa and CrowdStrike
Why It's a Strong Regulatory Compliance Option
Hyperproof is one of the strongest choices for the specific job of proving compliance repeatedly. Reviewers describe maintaining a comprehensive record of changes and detailed tracking of all approvals, which is what an auditor asks for and what most teams assemble by hand.
Cross-framework mapping is the second argument, and it compounds. An organisation holding three certifications collects evidence once rather than three times, and the saving grows with each framework added.
The integration depth is the third. Pulling evidence automatically from the systems that generate it removes the most tedious recurring task in a compliance programme, and reviewers describe it as the capability that changed how they work.
Pros
Cross-framework control mapping so evidence satisfies multiple requirements at once
Automated evidence collection from connected technical systems
Audit readiness tracking that surfaces gaps ahead of the audit
Clean interface and centralised compliance workflows, praised consistently by reviewers
Three months to implement, the fastest among the governance tools here
Cons
Report customisation is described by multiple reviewers as challenging, with limited options
Initial setup is described as unintuitive and requiring careful attention
Framework customisation becomes complex to execute at scale
Several integrations are needed before the full picture is available
Built for evidence and certification rather than regulatory change monitoring
Customer Reviews
Hyperproof holds 4.5 out of 5 across 223 G2 reviews and 4.8 out of 5 across 116 Capterra reviews. Reviewers praise the ease of use and the centralisation of compliance management, with simplified evidence tracking and collection the most repeated theme. The interface and responsive customer support come up frequently, and one reviewer describes the product having changed how their company manages compliance over three years of use.
Criticism concentrates in two places. Report customisation draws repeated comment, with reviewers describing limited options and difficulty producing the exact output they need. Setup is the other theme, with reviewers calling the initial process unintuitive and noting that framework customisation requires real effort and support to execute well.

Final Verdict
Hyperproof is recommended for compliance teams managing multiple certification frameworks where evidence collection is the recurring cost. On that job it is among the strongest options available.
It is a weaker fit for in-house legal teams tracking regulatory change across jurisdictions. The product proves you are meeting requirements you already know about, and the work of discovering that a requirement changed sits outside it.
5. Diligent One Platform (formerly HighBond)

Overview
Diligent One Platform brings governance, risk, audit and compliance into a single environment, with board reporting as the distinguishing capability. The company's heritage is in board management software, and that shows in how information flows upward.
The platform spans several interconnected modules. Audit management, risk assessment, controls monitoring and data analytics each stand alone and share a common data layer, so a control failure surfaces in the audit module and the board report together.
Data analytics is the second heritage line, inherited from the ACL acquisition. Reviewers describe scheduling automated testing routines that run against operational data and flag exceptions without anyone opening a spreadsheet.
Ideal For
Enterprises reporting risk and compliance upwards to boards and audit committees
Organisations wanting audit, risk and compliance modules sharing one data layer
Teams running automated analytics against operational data as a control
Businesses already using Diligent for board management
Compliance functions with formal governance structures and defined reporting cycles
Top Features
Audit management with planning, fieldwork and issue tracking
Risk assessment and register with linkage into controls
Controls monitoring with automated testing routines against live data
Data analytics engine for exception testing at scale
Board and committee reporting built for governance audiences
Interconnected modules sharing a common data layer
Why It's a Strong Regulatory Compliance Option
Diligent One is one of the strongest choices where compliance has to be explained to a board. Reviewers describe clear, consistent reporting presented in a format governance audiences understand, which is a different output from the operational dashboards most of this category produces.
Automation through analytics is the second argument. Reviewers describe scheduling robots that run monthly, automatically start results workflows and identify potential exceptions that would otherwise require manual review across whole data sets.
Breadth is the third. Covering governance, risk, audit, compliance and board reporting in one place removes several vendor relationships, which matters more to a procurement function than any individual feature comparison.
Pros
Audit, risk, compliance and board reporting in one interconnected environment
Automated analytics routines that test operational data and flag exceptions
Reporting built for boards and audit committees rather than only operational teams
Templates and framework creation tools that speed up programme setup
Three months to implement, fast for a platform of this breadth
Cons
Reviewers describe some modules as inflexible and less configurable
Occasional bugs are reported, though reviewers note they are addressed with follow-up
Limited formatting and functionality within questionnaires, according to several reviewers
Release notes are hard to locate, which one reviewer describes as a recurring time cost
No regulatory monitoring, so changes must arrive from another source
Customer Reviews
Diligent One Platform holds 4.3 out of 5 across 161 G2 reviews and 4.5 out of 5 across 68 Capterra reviews. Reviewers praise the ease of use and the comprehensive feature set, singling out the ability to streamline governance, risk and compliance processes in one place. Implementation support draws specific praise, and several reviewers describe the automation of recurring testing as the capability that justified the purchase.
The criticisms are consistent across both platforms. Reviewers describe limited flexibility and configurability in certain modules, with one calling inflexibility the primary problem and noting that new users find the structure confusing before they learn it. Occasional bugs and limited questionnaire functionality are the other recurring themes.

Final Verdict
Diligent One Platform is recommended for enterprises with formal governance structures, where compliance has to be reported to a board and audit sits alongside it. The breadth and the reporting are genuinely strong for that audience.
It is less suitable for teams needing configuration flexibility or regulatory change detection. Reviewers are clear that some modules resist adaptation, and the product assumes requirements arrive from elsewhere rather than discovering them.
To find out how LEGALFLY could work for you, schedule a call with one of our experts.
6. NAVEX One

Overview
NAVEX One approaches compliance from the ethics and policy direction. Policy management, whistleblowing hotlines, compliance training, incident management and third-party risk sit in one platform, built around the idea that compliance is as much about conduct as about controls.
Policy management is the centre of gravity. Documents are published, distributed to the right populations, attested to and tracked, which is the mechanism most organisations use to prove that staff were told about a requirement.
The ethics reporting side has the longest history, and NAVEX has been a reference name in whistleblowing hotlines for years. That part of the business is why many organisations already have a relationship with the vendor before compliance comes up.
Ideal For
Organisations running policy management and attestation at scale
Compliance functions with ethics reporting and whistleblowing obligations
Businesses needing compliance training tied to policy distribution
Teams managing incidents and investigations alongside compliance obligations
Enterprises with existing NAVEX hotline relationships extending into wider compliance
Top Features
Policy management with distribution, versioning and attestation tracking
Whistleblowing and ethics reporting with case management
Compliance training assigned and tracked against policy requirements
Incident management and investigation workflows
Third-party risk assessment and monitoring
Risk insights connecting policy acknowledgements, training records and incidents
Why It's a Strong Regulatory Compliance Option
NAVEX One is one of the smartest choices where the compliance obligation is about people rather than systems. Reviewers describe the ability to get necessary information to staff and ensure associates are notified of rules and regulations, which is the attestation evidence a regulator asks for.
The connected data is the second argument. One reviewer describes the platform connecting policy acknowledgements, training completion, incident reports and third-party risk assessments into a view of the company's risk environment that fragmented reporting cannot produce.
Document accessibility is the third, and it is more valuable than it sounds. Reviewers describe finding company-wide policies in one place and searching for a specific rule rather than asking someone where it lives.
Pros
Policy distribution and attestation tracking across large and varied populations
Ethics and whistleblowing case management in the same system as policy
Compliance training tied directly to policy requirements
Connected data across policy acknowledgements, training records and incidents
Centralised document access that reviewers describe as easy to search
Cons
Reviewers describe the interface and menu organisation as unintuitive, with some users reluctant to use it at all
Support responsiveness draws repeated and specific criticism
Setup and configuration of the full platform requires substantial time or outside help
Reviewers report missing alerts on assigned policy reads
Attestation flows are described by some reviewers as more complicated than necessary
Customer Reviews
NAVEX One holds 3.7 out of 5 across 87 G2 reviews and 3.9 out of 5 across 22 Capterra reviews, the lowest ratings in this comparison. Positive reviewers praise the centralised policy management, the ease of finding company-wide documents, and the breadth of a platform covering corporate risk, compliance and conduct in one place. One reviewer describes it as a one-stop shop that made employee tracking considerably easier.
The negative reviews are specific and worth reading before shortlisting. Interface and menu organisation draw repeated criticism, with one reviewer describing users as turned off to the point of avoiding the application. Support responsiveness is the other consistent theme, with reviewers describing cases that go unanswered and information having to be repeated across channels.

Final Verdict
NAVEX One is recommended for organisations whose compliance obligations centre on policy, conduct and training, particularly where an ethics hotline relationship already exists. For that use case the breadth is real and the alternatives are thin.
It is harder to recommend on the strength of its reviews alone. The interface and support criticisms are frequent and consistent enough to warrant reference checks with organisations of your size, and the product does no regulatory monitoring at all.
7. Thomson Reuters Regulatory Intelligence

Overview
Thomson Reuters Regulatory Intelligence is the incumbent in regulatory content, built on the editorial operation behind the wider Thomson Reuters business. It tracks regulatory developments across global markets and pairs the raw change data with analysis written by people who understand what the change means in practice.
The product is aimed squarely at financial institutions. Content is organised around the regulators that matter to banks, insurers and asset managers, and the obligation libraries reflect that orientation rather than a general corporate one.
Brand weight is part of what is being bought. When a compliance function has to defend its monitoring approach to a board or a supervisor, the Thomson Reuters name does work that a newer vendor's cannot.
Ideal For
Large banks, insurers and asset managers with formal regulatory monitoring obligations
Compliance functions that need expert commentary alongside the change itself
Organisations already using Thomson Reuters research and practical guidance products
Teams defending their monitoring approach to supervisors and boards
Global institutions tracking developments across many financial jurisdictions
Top Features
Global regulatory change feeds across financial services regulators
Analyst commentary interpreting what a change means in practice
Obligation libraries structured for financial services compliance
Alerting and reporting for regulatory change workflows
Integration with the wider Thomson Reuters research estate
Why It's a Strong Regulatory Compliance Option
Thomson Reuters is one of the strongest choices where editorial depth is the requirement. A raw feed tells you a rule published, and an analyst note tells you whether it changes anything for an institution like yours, which is a different and more expensive thing to produce.
Credibility is the second argument, and it is not a soft one. Thomson Reuters interpretation of a regulatory change frequently becomes the reference point other people work from, including the people who will review your compliance programme.
Pros
Editorial analysis alongside the regulatory data, which few competitors attempt
Deep coverage of financial services regulators globally
Established standing with supervisors, boards and legal buyers
Fits naturally alongside other Thomson Reuters research products
Long operating history in regulatory content
Cons
Built around financial services, so the fit weakens for manufacturing, technology or healthcare
Impact mapping to your own contracts and policies remains a manual exercise
Heavyweight for in-house legal teams that need monitoring as one capability among several
The commercial model suits large institutions rather than lean compliance functions
No workflow to carry a change through to an updated document
Final Verdict
Thomson Reuters Regulatory Intelligence is recommended for large financial institutions that need authoritative regulatory content with expert interpretation, and that have the compliance headcount to act on it.
It is a weaker fit for in-house legal teams outside financial services, and for any team whose bottleneck is connecting change to their own documents. The product is built to tell you what happened, in considerable depth, and the work after that stays with your people.
8. Wolters Kluwer OneSumX Regulatory Change Management

Overview
OneSumX Regulatory Change Management approaches the problem from the controls side. Regulatory content is curated and structured, then mapped to the internal controls and obligations a financial institution already maintains, so a change surfaces against the specific control it affects.
That design assumes a mature compliance function. There has to be a controls library to map to, with owners attached and testing schedules behind it, which is normal in a bank and unusual almost everywhere else.
Wolters Kluwer brings editorial heritage comparable to Thomson Reuters, with a stronger orientation towards finance, risk and regulatory reporting as a connected set rather than as separate products.
Ideal For
Banks and insurers with an established internal controls library
Compliance functions running formal regulatory change governance
Institutions already using OneSumX for finance or risk reporting
Teams needing audit-ready evidence that change was assessed and actioned
Organisations where regulatory change management is a defined programme
Top Features
Curated regulatory content structured for financial services
Mapping from regulatory change to internal controls and obligations
Workflow for assessment, assignment and sign-off
Audit reporting across the change management process
Connection to the wider OneSumX finance and risk suite
Why It's a Strong Regulatory Compliance Option
OneSumX is one of the smartest choices for institutions whose problem is governance rather than awareness. Mapping change to a controls library turns monitoring into an auditable process, which is what a supervisor actually asks to see when they review your programme.
The suite argument is the second one. For an institution already running OneSumX for regulatory reporting, adding change management to an existing relationship avoids another vendor assessment and another security review.
Pros
Controls mapping that turns monitoring into auditable governance
Strong curated content for banking and insurance regulation
Fits institutions with formal three-lines-of-defence structures
Established vendor with deep financial services standing
Connects to wider finance and risk reporting capabilities
Cons
Requires an existing controls library, which many organisations do not have
Financial services taxonomies make it an awkward fit in other sectors
Implementation effort is substantial relative to lighter monitoring tools
No connection to your contracts, so document-level impact stays manual
Assessment workflow stops short of producing the updated document
Final Verdict
OneSumX Regulatory Change Management is recommended for banks and insurers with a controls library, formal governance and the programme resource to run it properly. In that setting the controls mapping is genuinely valuable.
It is a poor fit for lean in-house legal teams. The product assumes an operating model that exists in regulated financial institutions and almost nowhere else, and without that structure most of its value is inaccessible.
9. LexisNexis Regulatory Compliance

Overview
LexisNexis Regulatory Compliance breaks regulation into obligations rather than documents. Instead of alerting you that an act was amended, it maintains registers of the specific duties that apply to a business activity and flags when one of those duties changes.
That framing suits operational businesses. A logistics company cares less about the shape of a statutory instrument than about whether its driver licensing duties moved, and the obligation register answers the second question directly.
Coverage is strongest in a defined set of jurisdictions, with the United Kingdom and Australia particularly well developed, reflecting where the product was built out first.
Ideal For
Compliance teams managing obligations tied to specific business activities
Operational businesses in transport, energy, healthcare and manufacturing
Organisations needing an obligations register they can assign and evidence
UK and Australia-centred businesses where coverage is deepest
Teams that think in duties rather than in legislation
Top Features
Obligation registers mapped to business activities
Jurisdiction-specific regulatory content maintained by legal editors
Change alerts at the obligation level
Assignment and evidencing of obligation ownership
Access to the wider LexisNexis legal research estate
Why It's a Strong Regulatory Compliance Option
LexisNexis is one of the strongest choices where the requirement is operational compliance rather than financial regulation. Obligation-level granularity means the output arrives in the form an operations manager can act on without a lawyer translating it first.
The editorial base is the second argument. LexisNexis maintains legal content at scale, and the obligation registers inherit that maintenance discipline rather than relying on automated extraction alone.
Pros
Obligation-level content that operational teams can act on directly
Strong editorial maintenance behind the registers
Suits regulated operational sectors outside financial services
Assignment and evidencing built around the obligations themselves
Backed by one of the largest legal content operations in the market
Cons
Coverage depth varies considerably by jurisdiction, so multi-region teams must test their own list
Obligation registers require configuration against your activities before value appears
No view of your contracts, so document-level impact remains manual
Interface and workflow are less modern than newer entrants in the category
No capability to produce the updated policy or contract once a duty changes
Final Verdict
LexisNexis Regulatory Compliance is recommended for operational businesses in regulated sectors, particularly in the UK and Australia, where obligations rather than legislation are the working unit.
It is less suitable for multi-jurisdiction organisations whose regulatory footprint sits outside the well-developed coverage areas. Check your own jurisdiction list against the register before shortlisting, because that single test decides the product's usefulness.
10. Regology

Overview
Regology positions itself as an AI-led approach to regulatory intelligence, with a law library maintaining regulatory content and an assistant layer that answers questions against it. The pitch is that compliance teams should be able to ask what applies to them rather than reading a feed and working it out.
The product covers discovery of applicable regulation, mapping to obligations, and task assignment when something needs doing. Compliance tracking and document management are the capabilities buyers rate as most critical, which tells you where the product's weight sits.
It is aimed at mid-sized and enterprise organisations rather than small businesses, with web deployment only and support through email, phone and a knowledge base.
Ideal For
Compliance teams wanting conversational access to regulatory content
Organisations building an obligation library from scratch
Mid-market and enterprise businesses without a dedicated regulatory intelligence function
Teams assigning and tracking regulatory tasks alongside monitoring
Businesses wanting AI assistance without an enterprise implementation
Top Features
AI-led discovery of regulations applicable to the organisation
Law library maintaining regulatory content across jurisdictions
Obligation mapping with task assignment and tracking
Alerts and escalation when tracked regulations change
Compliance tracking, audit trail and archiving for evidence purposes
Third-party integrations for monitoring regulatory obligations
Why It's a Strong Regulatory Compliance Option
Regology is one of the smartest choices for teams that find the established suites heavier than their problem. The interface assumes a compliance manager rather than a regulatory intelligence analyst, which widens who in the organisation can actually use it.
The discovery capability is the second argument. For an organisation that does not yet know its full regulatory footprint, working out what applies is a genuine first problem, and most incumbents assume you already have that answer.
Pros
Modern interface that a compliance generalist can operate without specialist training
AI assistant reduces the reading burden on the regulatory library
Discovery helps organisations establish what actually applies to them
Obligation mapping and task tracking in the same product
Lighter implementation than enterprise governance suites
Cons
Enterprise governance features are thinner than the financial services suites
AI-led content maintenance should be tested against jurisdictions your team knows well
Smaller vendor, which procurement will weigh on continuity grounds
No connection to your contracts, so document impact remains manual
Web deployment only, with no mobile applications
Final Verdict
Regology is recommended for mid-market and enterprise businesses that need to establish and track their regulatory footprint without standing up a formal programme. The discovery capability answers a problem the incumbents assume away.
It is less suitable where formal governance, controls testing and audit evidence are the requirement. Those capabilities sit deeper in the GRC platforms on this list, and a compliance function with a three-lines-of-defence structure will find Regology covering the front of the process rather than all of it.
What Makes Good Regulatory Compliance Software?

The best regulatory compliance software is separated by what happens after the alert, not by how many sources it watches or how many frameworks it ships with. Coverage and framework libraries are where vendors compete. Impact analysis is where teams struggle.
The five criteria below are written as outcomes rather than feature checkboxes. Each one is testable in a demo.
1. It Covers the Jurisdictions You Actually Operate In
Headline source counts mean little on their own. A product monitoring thousands of sources is no use if it covers three of your seven markets properly and skims the rest.
Write down every jurisdiction where you hold a licence, employ people or sign contracts. Then ask each vendor to show live coverage for the three you consider most awkward, rather than the ones they lead with, and check what kinds of source sit behind it. Official gazettes, supervisory authorities, national banks, courts and official legal databases are a different evidence base from secondary commentary.
2. It Tells You What Changed for You, Not Only What Changed
A regulatory feed reports a publication. Useful software reports the consequence, which means a plain-English summary, an assessment of the business impact and a recommended next step rather than a link to a gazette entry.
Ask to see the output for a change you already handled. If your team's assessment took two days and the tool would have reached the same conclusion on its own, that difference is the value, and it is measurable rather than theoretical.
3. It Reads Your Own Contracts and Policies
This is the criterion most products fail, and it is the expensive one. Once a rule changes, somebody has to work out which contracts, policies and templates now conflict with it.
Ask directly whether the tool can test a new requirement against your own documents, and ask to see it happen on a document you bring. Most regulatory intelligence products have no view of your paper at all, and most governance platforms know your controls but not your contracts, so the mapping lands back with your team either way.
4. It Carries the Change Through to a Redraft and an Approval
Knowing which documents are affected is still not the finish line. The change becomes real when the wording is updated, a reviewer approves it and the new version replaces the old one in the system where people look for it.
Software that identifies the affected documents, produces the redraft and routes it for approval closes that loop. Software that emails you a list of affected items starts a project instead, and the project is where compliance capacity disappears.
5. It Leaves an Audit Trail Somebody Else Can Follow
When a supervisor asks how you knew about a change and what you did, the answer needs to exist in a system rather than in somebody's inbox. Every step should be logged: what was detected, who assessed it, what was decided, which documents were updated and who approved them.
Test this by asking for the evidence pack rather than the dashboard. A product built for supervised environments produces it without a services engagement, and one that cannot will cost you time at exactly the moment you have least of it.
To find out how LEGALFLY could work for you, schedule a call with one of our experts.
How to Choose Between the Best Software for Regulatory Compliance

1. Establish Whether Your Gap Is Monitoring, Impact or Evidence
These three feel like one problem and have different answers. If your team genuinely misses changes, you need broader monitoring and the regulatory intelligence suites here are strong at it. If you collect the same evidence three times for three frameworks, you need a governance platform.
If you find out about changes in good time but then lose two weeks working out what they touch, neither of those buys you anything. That middle gap is where most in-house legal and compliance teams actually sit, and it is the one fewest products address.
Ask your compliance lead which of the three described the last three regulatory changes you handled. The answer usually settles the shortlist in a single conversation.
2. Test Against a Change You Have Already Handled
Pick a regulation your team worked through in the last year, ideally one that was awkward and touched several documents. Ask each vendor to show what their product would have produced at each stage.
You know the right answer, the real timeline and the documents it affected. That makes it the only evaluation where you can grade the output rather than take the demo on trust, and it exposes the difference between a tool that alerts and a tool that acts.
3. Count the Steps That Stay Manual
Map your current process from detection through to an updated, approved document. Then mark which steps each product removes and which it leaves with your team.
Many tools remove the first step and none of the rest. That is worth knowing before the business case is written, because the time saving you can claim is only as large as the steps that genuinely disappear.
4. Check Whether It Reads Your Own Paper
Ask each vendor whether the tool can test a regulatory change against your contracts and policies, then ask to watch it happen. Be alert to answers that describe an integration where you export documents somewhere else and import the results back.
This is the biggest dividing line in the category. A product that monitors the outside world, a product that manages your controls, and a product that reads your own documents against a new rule are solving three different problems, and only the third removes the work your team is actually doing.
5. Ask What Happens Across Several Hundred Documents at Once
A new requirement rarely touches one contract. When a rule changes, the question is whether every affected agreement in the portfolio can be checked against it inside the compliance window.
Ask each vendor how a team would review an entire data room or contract set against a single new requirement, and how long that takes. A tool that handles one document at a time is a tool that will not finish before the deadline.
6. Get Security Involved in Week One
If the tool is going to read your contracts and policies, the security review applies in full. Bring your CISO or IT security lead into the first round rather than month four, when a failed review means starting the evaluation again.
They need three answers: what happens to a document before a model reads it, where data is processed and stored, and which deployment models are offered. Single-tenant, regional data residency and on-premise processing change which vendors survive that conversation, and vendors that cannot answer clearly at the first meeting rarely improve by the third.
7. Decide Whether You Want a Point Tool or a System
A specialist regulatory feed or a standalone governance platform is a single-purpose purchase that sits alongside everything else your legal and compliance teams use. A legal operating system handles monitoring as one capability among contract review, drafting and document management.
The second option means one vendor assessment, one security review and one set of integrations rather than three. For lean teams that consolidation is often worth more than a marginal gain in source coverage or framework count.
To find out how LEGALFLY could work for you, schedule a call with one of our experts.
Everything You Need to Know About Regulatory Compliance Monitoring
Category | Key Considerations |
Top 3 options | LEGALFLY for in-house legal and compliance teams needing change connected to their own documents, Optro for audit-led compliance programmes with controls testing, Thomson Reuters Regulatory Intelligence for editorial depth in financial services |
Best overall option | LEGALFLY. Legal Radar covers 130+ jurisdictions and tests each change against your own contracts and policies, with redrafting and approval in the same system |
Why teams replace their current tool | Monitoring and governance sit in separate products, impact analysis stays manual, and nothing connects a detected change to the contracts and policies that have to be updated |
How to choose | Establish whether your gap is monitoring, impact or evidence, test against a change you have already handled, count the steps that stay manual, and involve security in week one |
Ease of switching | Days to weeks for tools that run inside Microsoft 365, since there is no content library or controls structure to migrate. Governance platforms run three to four months and usually require taxonomy and controls alignment |
Must-have features | Coverage of your actual jurisdictions, plain-English impact assessment, testing against your own documents, bulk review across a portfolio, redraft and approval workflow, and an audit trail a supervisor can follow |
Mistakes you should not make | Buying on headline source or framework counts, evaluating on the vendor's sample regulation, leaving security until month four, and assuming an alert is the same thing as an action |
Ready to Act on Regulatory Change, Not Just Track It? Try LEGALFLY
Three things separate LEGALFLY from everything else on this list:
Legal Radar monitors 130+ jurisdictions and tests each change against your own contracts and policies rather than reporting it in the abstract.
Whole workflows then carry that change through to a redrafted document and legal sign-off, with an audit trail at every step. Every document is anonymised before analysis begins, on an architecture designed before the current model generation rather than added later.
It is built for one buyer in particular: the in-house legal or compliance team inside a regulated enterprise, operating across several jurisdictions, facing the EU AI Act, DORA, NIS2, CSRD and CSDDD with the same headcount as last year.
Bring a regulatory change your team has already worked through to a demo of our legal AI software, then compare what comes back against what it actually cost you.
You can also see how contract intelligence keeps the obligations inside those contracts visible once the change lands.
To find out how LEGALFLY could work for you, schedule a call with one of our experts.
FAQs About Regulatory Compliance Monitoring Software
What is regulatory compliance monitoring software?
Regulatory compliance monitoring software tracks changes from regulators, legislatures, courts and official publishers, then helps an organisation assess what each change affects and prove that someone acted on it. Better products add impact assessment, obligation mapping and an audit trail rather than stopping at the alert. LEGALFLY's Legal Radar covers 130+ jurisdictions across official gazettes, supervisory authorities, national banks, courts and official legal databases, and tests each change against the customer's own contracts and policies.
What is the best software for regulatory compliance in 2026?
The best software for regulatory compliance in 2026 is LEGALFLY, for in-house legal and compliance teams of 3 to 200 people inside enterprises of 200 to 100,000 employees. Legal Radar monitors 130+ jurisdictions and delivers plain-English summaries with business impact and recommended next steps, then identifies the affected documents in SharePoint or Google Drive, redrafts them and routes the redraft for approval. The differentiator no competitor replicates is anonymisation applied at import, before any model reads the document.
What should I consider when choosing the right regulatory compliance software for me?
Consider five things when choosing regulatory compliance software: coverage of the jurisdictions you actually operate in, plain-English impact assessment rather than a link to a gazette, the ability to test a change against your own contracts and policies, a redraft and approval workflow, and an audit trail a supervisor can follow. The third is where most products stop, because regulatory feeds have no view of your documents and governance platforms know your controls rather than your paper. Test each shortlisted tool against a regulatory change your team already worked through, since you know the right answer and the real timeline.
How does LEGALFLY differ from similar alternatives?
LEGALFLY differs from similar alternatives because monitoring connects to your own documents instead of ending at the alert or the control. Legal Radar covers 130+ jurisdictions, tests each change against your contracts and policies, identifies the affected documents across SharePoint, Google Drive and LEGALFLY, redrafts them and routes the redraft for legal approval. Optro, LogicGate, Hyperproof, Diligent One and NAVEX One manage controls, evidence and policy but do no regulatory monitoring, while Thomson Reuters, Wolters Kluwer and LexisNexis monitor regulation but never read your paper. LEGALFLY also handles contract review, drafting and legal research in the same system, so monitoring is one capability rather than another single-purpose tool.
How do I get started with LEGALFLY?
Getting started with LEGALFLY begins with a scoped demo and a discovery conversation, since the evaluation is sales-led rather than self-serve. Bring a regulatory change your team has already worked through, along with the contracts and policies it affected, so the output can be graded against what the work actually cost you. Deployment is measured in days, and Agristo saw results within days of a single kickoff. Most teams begin with one jurisdiction set and one playbook before extending across the rest of the estate.
How easy is it to switch to LEGALFLY?
Switching to LEGALFLY is straightforward because there is no regulatory content library or controls structure to migrate and no new interface for the team to learn. It runs inside Word, Outlook, Teams, SharePoint, Google Drive, Slack and NetDocuments, with anonymisation applied automatically in each. Teams typically run it alongside an existing feed for one regulatory cycle, comparing what each surfaces before switching fully. That parallel period is also the cleanest way to test coverage on the jurisdictions you care about most.
We already have a GRC platform. Why do we need regulatory compliance monitoring software?
A governance platform manages the obligations you already know about, and regulatory compliance monitoring software of this kind tells you when those obligations change. Controls libraries, evidence collection and audit programmes all assume the requirement is already in the system, so something has to put it there and keep it current. Legal Radar covers 130+ jurisdictions and tests each change against your own contracts and policies, then carries the update through to a redrafted document. The two sit alongside each other, with monitoring feeding the governance programme rather than replacing it.
Is our data safe if the software reads our own contracts?
Data safety is the right question to ask once a tool reads your contracts rather than only public sources, and it decides most evaluations in regulated industries. LEGALFLY anonymises documents before analysis begins, with names, roles, company details and identifiers pseudonymised at import so identifiable data never reaches a third-party model. Security follows a framework aligned with ISO 27001, SOC 2 Type II and GDPR, with annual independent penetration testing and every step logged. Deployment runs from SaaS to single tenant in your preferred Azure region, and single tenant with on-premise anonymisation where identifiable data never leaves your environment.
Disclaimer: This comparison reflects publicly available product information and verified user reviews as of October 2026. Compliance and legal technology products change quickly, so for the most up-to-date details on features, coverage and availability, please check directly with each provider.

