




NIS2 is a directive, not a regulation, and that single fact is why most compliance tools do not solve it.
A regulation applies identically everywhere. A directive is transposed into national law by each member state, which means an organisation operating across Europe faces as many variants of NIS2 as it has countries, with different registration deadlines, different incident thresholds and different enforcement regimes.
The security controls are the easy part. Risk management measures under Article 21 overlap heavily with ISO 27001, and the compliance automation platforms on this list handle them well.
LEGALFLY is the best NIS2 compliance software for the legal half, which is the supply chain security clauses in your supplier contracts, the policies behind your measures, and tracking what twenty-seven member states did with the same directive.
Every entry draws on factual G2 and Capterra reviews and a detailed analysis of each tool in October 2026.
To find out how LEGALFLY could work for you, schedule a call with one of our experts.
Key Takeaways (TL;DR)
What NIS2 Is: The second Network and Information Security Directive, which extended EU cybersecurity law across energy, transport, banking, health, water, digital infrastructure, public administration, manufacturing, food, waste and postal services. Because it is a directive, it binds you through your member state’s own transposition, and essential and important entities face different levels of supervision.
What NIS2 Compliance Software Does: Helps essential and important entities meet the second Network and Information Security Directive across risk management measures, supply chain security, incident reporting and management accountability, as transposed into each member state's national law.
What Most Compliance Software Misses: Controls tooling covers Article 21's security measures and stops there. Supply chain security clauses still have to be negotiated into supplier contracts one at a time, policies have to be drafted and maintained, and nothing tracks what each member state did with the directive.
Best Overall NIS2 Compliance Tool: LEGALFLY, for the legal and contractual layer. Multi Review checks an entire supplier contract estate against your required security provisions in one pass, Review produces the amendment language, Discovery produces the policies, and Legal Radar monitors 130+ jurisdictions, which covers the national transpositions individually.
What Sets LEGALFLY Apart: Whole legal workflows run end to end, from a national transposition or a contractual gap through review and redrafting to legal approval, on documents that are anonymised before analysis begins, on an architecture designed before the current generation of models existed. No competitor on this list replicates that combination.
How to Choose: Work out whether your gap is security controls, supplier contracts or multi-jurisdiction tracking, because three different categories of product answer those three problems.
Best NIS2 Compliance Tools in 2026 at a Glance
Tool | Best For | Key Features | Pros | Cons |
LEGALFLY | In-house legal and compliance teams handling supply chain clauses and multi-jurisdiction tracking | End-to-end agentic workflows through Agent Studio, anonymisation before analysis, Contract Intelligence across the lifecycle, Multi Review across data rooms, Legal Radar across 130+ jurisdictions | Checks an entire supplier contract estate against required security provisions in one pass; tracks national transpositions individually; anonymisation applied at import | Sales-led evaluation, and it is the legal layer rather than a controls platform |
DataGuard | European organisations wanting platform and expert consultant together | ISO 27001, TISAX, NIS2, SOC 2, GDPR and EU AI Act coverage, iterative risk management, automated evidence collection, named consultant | Names NIS2 explicitly in its framework coverage, with consultants reviewers praise by name | Reviewers describe a confusing interface and templates that can feel rigid |
Vanta | Organisations wanting the broadest framework coverage and integration estate | Automated evidence collection, 35+ frameworks, continuous monitoring, risk management, Trust Center | 122 verified integrations and the largest review base in this comparison | Reviewers report noisy notifications and inflexible contract terms for smaller teams |
Drata | Teams running NIS2 alongside ISO 27001 and SOC 2 | Automated evidence collection, continuous control monitoring, policy templates, risk assessment | 159 integrations, the highest of any platform here | Reviewers describe support that has shifted to AI agents and inconsistent test results |
OneTrust Tech Risk & Compliance | Large enterprises running NIS2 inside a wider GRC programme | Regulatory content, obligation mapping to actionable tasks, risk management, third-party risk, policy management | Turns complex regulations into tasks that fit existing processes, with strong automation | Reviewers consistently describe complex setup and a steep learning curve |
ISMS.online | Organisations wanting a structured management system rather than evidence automation | Assured Results Method, pre-built documentation, risk register, policy packs, incident and CAPA tracking | Built around the management system, with reviewers reporting auditors praising their documentation | 10 integrations, and reviewers describe modules that do not share data |
Sprinto | Fast-growing companies certifying quickly with heavy support involvement | Automated evidence collection, 200+ standards, policy templates, security training automation | Reviewers repeatedly describe certification completed ahead of deadline | Reviewers describe clunky navigation and support that slowed after year one |
Secureframe | Small and mid-sized teams wanting guided onboarding | Automated evidence collection, continuous monitoring, Comply AI, Trust Center, policy templates | Customer success managers are the single most praised element across its review base | Only 44 verified integrations, the fewest here |
Hyperproof | Compliance teams managing NIS2 alongside several other frameworks | Control framework management, cross-framework mapping, automated evidence collection, audit readiness | Cross-framework mapping so NIS2 evidence satisfies overlapping ISO 27001 requirements | Report customisation difficulty and setup reviewers describe as unintuitive |
LogicGate Risk Cloud | Teams building NIS2 workflows to their own process | No-code workflow builder, risk register, controls mapping, third-party risk, incident workflows | Configurable to any process, consolidating controls, supply chain and incident reporting | Steep learning curve and nothing pre-configured for NIS2 |
Why Organisations Need NIS2 Compliance Software
NIS2 widened the scope of European cybersecurity regulation dramatically. Where its predecessor covered a narrow set of operators, NIS2 reaches energy, transport, banking, health, water, digital infrastructure, public administration, manufacturing, food, waste and postal services.
The entity classification matters because the obligations differ. Essential entities face proactive supervision, important entities face reactive supervision, and both face the same Article 21 security measures.

What NIS2 Compliance Software Does
Article 21 sets out the risk management measures, covering risk analysis, incident handling, business continuity, supply chain security, secure development, cryptography, access control and multi-factor authentication. That list maps closely onto ISO 27001, which is why compliance automation platforms address it well.
Incident reporting is a separate operational obligation. An early warning within twenty-four hours, a notification within seventy-two, and a final report within a month, with thresholds that vary by national transposition.
Management accountability is the third pillar and it is new. Article 20 makes management bodies responsible for approving the measures and overseeing implementation, with personal liability available in several transpositions.
Where Most NIS2 Tools Fall Short
Supply chain security is the obligation tooling does not reach. Article 21 requires security in supplier and service provider relationships, and that means provisions in the contracts with those suppliers.
A controls platform knows your vendors exist. It does not know whether the agreement with each one says anything about security requirements, incident notification obligations, audit rights or subcontracting limits.
The twenty-seven transpositions are the second gap. Member states implemented the directive on different timetables with different registration mechanisms, different incident thresholds and different penalty regimes, and almost no tool tracks them individually.
Policy drafting is the third. The measures under Article 21 need documented policies behind them, and template policies drift the moment they are adopted because updating them is nobody's weekly job.
Best NIS2 Compliance Software Overall

LEGALFLY is the best NIS2 compliance software for the legal and contractual layer, and it is deliberately not a controls platform. For Article 21's technical measures and the evidence behind them, the compliance automation products on this list do work we do not attempt.
What we do is the contracts and the jurisdictions. Multi Review ingests an entire supplier contract estate from SharePoint or your document system, applies one playbook across every file, flags missing security provisions, absent incident notification obligations and unrestricted subcontracting, and exports an audit-ready summary with every finding linked to its source clause.
Legal Radar handles the transposition problem. It monitors official regulators and publishers across 130+ jurisdictions and tests each change against your own contracts and policies, which means twenty-seven national implementations are tracked individually rather than as one directive.
LEGALFLY helps your team move faster: less time buried in contracts, more time on the work that actually matters. Book a call to see it in action.
Best NIS2 Compliance Tools: In-Depth Review & Comparison
The ten tools split into three groups. There are compliance automation platforms built around controls and evidence, enterprise GRC platforms that carry NIS2 as one obligation among many, and the legal layer that reads the contracts and tracks the national laws.
Each entry covers what the product does, who it fits, its strongest capabilities, why it belongs here, what reviewers say, and where it stops.
1. LEGALFLY

Overview
LEGALFLY is the legal operating system for corporates. It gives in-house teams AI-native workflows for intake, contract review, drafting, due diligence and legal research, with security and anonymisation underneath all of it.
For NIS2, the legal work splits across supplier contracts and twenty-seven national laws.
Article 21's supply chain expectations have to appear as provisions in agreements with suppliers, and the directive itself exists in practice only as the version each member state transposed. Multi Review handles the first across an entire estate, and Legal Radar monitors the second jurisdiction by jurisdiction.
Our customers sit squarely inside NIS2's expanded scope. Bosch and SAP in manufacturing and digital infrastructure, Lufthansa in transport, MSIG Europe and Group Foyer in financial services, plus a partnership with the European Commission's HR Directorate-General.
We hold ISO 27001 and SOC 2 Type II certification, with security following a framework aligned with both plus GDPR and annual independent penetration testing.
To find out how LEGALFLY could work for you, schedule a call with one of our experts.
Ideal For
In-house legal and compliance teams of 3 to 200 supporting enterprises of 200 to 100,000 employees
Essential and important entities whose NIS2 gap is supplier contracts rather than security controls
Organisations operating across several member states and facing different transpositions
Teams drafting and maintaining the policies behind Article 21 measures
Entities running NIS2 alongside DORA, ISO 27001 or the EU AI Act, where contractual requirements overlap
Top Features
Agent Studio for end-to-end legal workflow automation. Workflows trigger from email, Slack, Teams or manually, conditional logic routes work and escalates when thresholds are met, approval steps sit wherever a decision is needed, and the right person is notified automatically.
Anonymisation before analysis. Names, roles, company details and identifiers are pseudonymised at import, with context and structure intact, so identifiable data never reaches a third-party model. This is applied by default rather than configured per workflow.
Contract Intelligence across the full lifecycle, from drafting and negotiation through approval and e-signature to renewals, expirations, notice periods and obligations. Announced with a waitlist open, launching October 2026.
Playbook-driven AI contract review with playbooks configured for Article 21's supply chain security expectations, covering security requirements, incident notification obligations, audit rights and subcontracting limits. 120+ lawyer-built playbooks across 100+ document types, plus a builder that generates a custom playbook from your own golden contracts in around two minutes.
Multi Review for bulk analysis across entire data rooms, applying one playbook to hundreds of supplier agreements at once and exporting audit-ready summaries with every finding linked to its source clause.
Legal Radar, regulatory tracking software monitoring official regulators and publishers across 130+ jurisdictions, which covers the national transpositions of NIS2 individually rather than as a single directive.
Discovery, AI for legal research grounded in 1000+ official legal sources across 130+ jurisdictions, with citations and auditable reasoning on every answer, plus AI contract drafting for producing new supplier agreements from your own templates..
Integrations with Microsoft Word, SharePoint, Outlook, Teams, Google Drive, Slack, NetDocuments and Microsoft Copilot, each carrying automatic anonymisation.
Why We're the Best NIS2 Compliance Tool for the Legal Layer
The honest version starts with what we are not. We do not run your risk management framework, we do not monitor your technical controls, and we do not file your incident reports. Those are security and operations disciplines and the platforms on this list handle them.
Supply chain security is the first argument. Article 21 requires security in supplier relationships, which means provisions in supplier contracts, and Multi Review checks an entire estate against your required provisions in one pass rather than one document at a time.
The transposition problem is the second and it is the one nobody else addresses. NIS2 is twenty-seven national laws wearing one name, and Legal Radar monitors regulators and publishers across 130+ jurisdictions, testing each change against your own contracts and policies.
Agent Studio is the third and it makes the first two operational. A transposition change or a contractual gap identifies the affected documents in SharePoint or Google Drive, redrafts them, routes the redraft for legal review and files the approved version, with an audit trail across every step.
Anonymisation is the fourth, and for an entity subject to NIS2 it matters more than usual. Documents are anonymised before analysis begins, which is the answer a security function wants when asked what happens to supplier contracts inside a third-party AI tool.

Pros
Multi Review checks hundreds of supplier agreements against your required security provisions in one pass
Legal Radar monitors 130+ jurisdictions, so the national transpositions are tracked individually and tested against your own documents
Review generates the amendment language and Discovery the policy updates, both against positions your legal team has approved
The documented measures behind Article 21 are written and maintained rather than adopted and forgotten
Documents are anonymised at import, with SaaS, single-tenant and on-premise deployment options
Cons
Sales-led evaluation, so the first step is a scoped demo and a discovery conversation rather than a self-serve trial
Not a controls or evidence platform, so Article 21's technical measures sit with the compliance automation tools on this list
Does not handle incident reporting workflows, which are an operational rather than a legal process
Customer Reviews
LEGALFLY holds 4.7 out of 5 across eight Capterra reviews, with value for money rated 4.8, customer service 4.7 and features 4.4. Reviewers describe faster document review and legal research across daily legal work.
What users highlight most is speed on document-heavy work and reliable answers on specific jurisdictions, which is the capability a multi-member-state NIS2 programme depends on.

Final Verdict
If your NIS2 gap is supplier contracts, policies or tracking what each member state actually did, this is the strongest option here. Those are legal documents and legal questions, and no controls platform addresses them.
If your gap is the Article 21 security measures themselves, buy a compliance automation platform. Most organisations end up running both, because NIS2 genuinely spans security and legal work.

2. DataGuard

Overview
DataGuard names NIS2 explicitly in its own framework coverage, alongside ISO 27001, TISAX, SOC 2, GDPR and the EU AI Act.
The model pairs software with named consultants. Reviewers describe their assigned expert by name far more often than they describe a feature, which tells you where the value sits.
The positioning is European. DataGuard is built around European regulatory frameworks rather than treating them as additions to a United States product.
Ideal For
European organisations wanting consultant support alongside a platform
Entities running NIS2 alongside GDPR, ISO 27001 and TISAX
Teams without internal information security or privacy specialists
Organisations preferring a retained expert over hourly external counsel
Top Features
Framework coverage naming ISO 27001, TISAX, NIS2, SOC 2, GDPR and the EU AI Act
Iterative risk management capturing risks, assets and controls
Automated evidence collection and control monitoring
Named consultant assigned to the engagement
External data protection officer service
Internal audit support with pre-audit gap identification
14 verified integrations including Jira, Asana, HubSpot, Airtable and Claude
Why It's a Strong NIS2 Option
Explicit NIS2 coverage is rarer than it should be. Most platforms address NIS2 by pointing at their ISO 27001 control set, and DataGuard names the directive in its own description.
Customer support is tagged 19 times and professional expertise 11 across 123 reviews, with helpful at 15, which is the signature of a service-led product rather than a software one.
Users describe the consultants as genuine sparring partners. A senior legal counsel describes their consultant as useful for audits, regulatory questions and day-to-day work, which is the kind of relationship a NIS2 programme actually needs.
Pros
Names NIS2 explicitly alongside ISO 27001, TISAX, SOC 2, GDPR and the EU AI Act
Named consultants are the most-praised element across the review base
Built around European regulatory frameworks rather than adapted to them
External data protection officer service available alongside
Reviewers describe it costing less than hourly external consultants
14 verified integrations and a two-month implementation average
Cons
Reviewers consistently describe the interface as confusing
Reviewers describe templates and workflows as rigid, with limited customisation
Feature limitations is the top-tagged weakness, with poor interface design and not intuitive behind it
One reviewer describes it as an off-the-shelf system unsuitable for every company
No view of what your supplier contracts actually say
Customer Reviews
DataGuard holds 4.6 out of 5 across 123 G2 reviews, with 90 at five stars and none below three.
G2's summary praises competent support and a user-friendly platform, naming guidance and quick responses from consultants, while noting navigation can be confusing at times.
The most useful review is the three-star one. A reviewer describes good advice and support from the external data protection officer service while criticising limited customisation and describing classic per-topic consulting as no longer the company's model, which is a fair description of a productised service.

Final Verdict
DataGuard is the strongest choice if you want a European platform with a named expert attached. The explicit NIS2 coverage and the consultant model together are a real differentiator.
Expect to work inside its structure. Reviewers are consistent that the templates are rigid and the interface is confusing, and it will not read your supplier contracts.
3. Vanta

Overview
Vanta is a compliance automation platform covering more than thirty-five frameworks, with NIS2 addressed through its security control set and continuous monitoring.
The product is built around removing manual evidence work. Access reviews, policy acceptance, vulnerability scanning and onboarding checks feed a readiness dashboard.
At 122 verified integrations it has the second-largest estate here, which decides how much of Article 21's evidence collects itself.
Ideal For
Organisations addressing NIS2 alongside ISO 27001, SOC 2 and GDPR
Teams with modern cloud infrastructure where automation has most to connect to
Mid-sized and larger companies that can absorb a two-month implementation
Security teams wanting the broadest integration coverage
Top Features
Automated evidence collection across 122 verified integrations
Continuous control monitoring with drift alerting
35+ framework support with cross-framework control mapping
Risk management covering register, assessment and treatment
Vendor risk management with automated security review workflows
Trust Center for publishing security posture
Policy templates mapped to control frameworks
Why It's a Strong NIS2 Option
Article 21's measures overlap substantially with ISO 27001, and Vanta's control mapping means addressing one addresses much of the other.
The review base is the largest in this comparison at 2,745, with compliance tagged 523 times and time-saving 405, which is the automation working at scale.
Vendor risk management is included, which covers the relationship management half of supply chain security even if it does not cover the contracts.
Pros
122 verified integrations, the second-highest in this comparison
35+ frameworks with cross-framework control mapping
The largest review base here at 2,745 G2 reviews
Vendor risk management and Trust Center included rather than sold separately
Ease of use is the most frequently tagged strength
Cons
Reviewers flag integration issues as the most common complaint, tagged 179 times
Pricing issues appear 146 times, with reviewers describing it as poorly suited to small organisations
Reviewers describe inflexible contract terms
Notification volume comes up repeatedly as a source of noise
No NIS2-specific coverage, and no view of supplier contract content
Customer Reviews
Vanta holds 4.5 out of 5 across 2,745 G2 reviews and 4.2 across 33 on Capterra, where value for money scores 3.9 against ease of use at 4.4.
G2's summary praises automated evidence collection and the intuitive interface, while noting pricing can be high for smaller organisations.
The critical reviews cluster around fit rather than function. A Capterra reviewer titles their review around the product not being startup-friendly, describing being locked into a contract after deciding the fit was wrong.

Final Verdict
Vanta is the strongest choice for the controls and evidence half of NIS2 if you also carry other frameworks. The integration estate and the review base are both category-leading.
It addresses NIS2 through ISO 27001 rather than directly. That covers Article 21 reasonably and leaves supply chain contracts and the national transpositions entirely untouched.
4. Drata

Overview
Drata has the largest integration estate in this comparison at 159, monitoring controls continuously and collecting evidence automatically across dozens of frameworks.
Drata Autopilot runs control tests on a schedule, flagging failures and maintaining an audit trail, so the control set's state is current rather than reconstructed.
The audit hub gives auditors direct access to evidence, which removes the export-and-exchange step entirely.
Ideal For
Organisations running NIS2 alongside ISO 27001 and SOC 2
Teams with complex estates where integration coverage decides how much automates
Companies wanting auditors working inside the platform
Security functions with internal capacity for the setup
Top Features
159 verified integrations, the highest count here
Drata Autopilot for continuous automated control testing
Policy templates with acceptance tracking
Risk assessment and register
Audit hub giving auditors direct evidence access
Personnel onboarding and offboarding compliance workflows
Why It's a Strong NIS2 Option
The integration count is the headline and it is a real advantage. Every integration is Article 21 evidence somebody does not collect by hand.
Users report clean audit outcomes, with several describing zero non-conformities at Stage 2, which is the only measure that matters.
Customer support is the most-tagged strength at 135 mentions, unusual in this category and ahead of ease of use.
Pros
159 verified integrations, the highest in this comparison
Reviewers report clean audit outcomes with no non-conformities
Customer support is the most frequently tagged strength
Audit hub removes evidence exchange with auditors
Continuous control monitoring with automated test scheduling
Cons
Support has shifted towards AI agents, with reviewers describing canned responses
Reviewers describe inconsistent control test results needing manual verification
The interface is described as overwhelming during initial setup
Reviewers mention clunky navigation and too many clicks
No NIS2-specific coverage and no view of contract content
Customer Reviews
Drata holds 4.7 out of 5 across 1,397 G2 reviews. Its Capterra listing shows 4.8 from six reviews, too small a sample to compare.
G2's summary praises ease of use and centralised compliance management, noting the interface can feel overwhelming during setup.
The sharpest criticism is about support rather than the product. One reviewer describes nearly every support interaction handled by AI agents giving generic responses, which sits oddly beside support being the most-praised element elsewhere.

Final Verdict
Drata is the right choice if integration coverage decides your purchase. More of your estate connects than with anything else here.
Weigh the support reports against how much help you will need. A first-time programme should ask directly what happens when an issue needs a human.
5. OneTrust Tech Risk & Compliance

Overview
OneTrust Tech Risk and Compliance is built to turn regulations into tasks. It takes complex regulatory requirements, maps them to business-ready content and guidance, and routes them as actionable work into existing processes.
The product sits inside OneTrust's wider platform, which covers privacy, third-party risk, policy management and ethics, and that breadth is both the strength and the cost.
It is an enterprise purchase. Reviewers are overwhelmingly from organisations above a thousand employees.
Ideal For
Large enterprises running NIS2 inside a wider GRC and privacy programme
Organisations already using OneTrust for privacy or third-party risk
Teams needing obligation mapping with regulatory content included
Companies with the capacity for a complex implementation
Top Features
Regulatory content with obligation mapping to actionable tasks
Risk management with contextualisation across the business
Third-party risk management
Policy management and attestation
Automated governance with business-ready guidance
Real-time dashboards and stakeholder reporting
AI-assisted risk assessments and evidence collection
Why It's a Strong NIS2 Option
Turning a directive into tasks is the right mechanism for NIS2. Article 21's measures are a list of obligations that have to become work with owners, and that translation is what the product does.
Automation is tagged 10 times and risk management 9 across 109 reviews, with ease of use leading at 13, which is a strong profile for an enterprise GRC product.
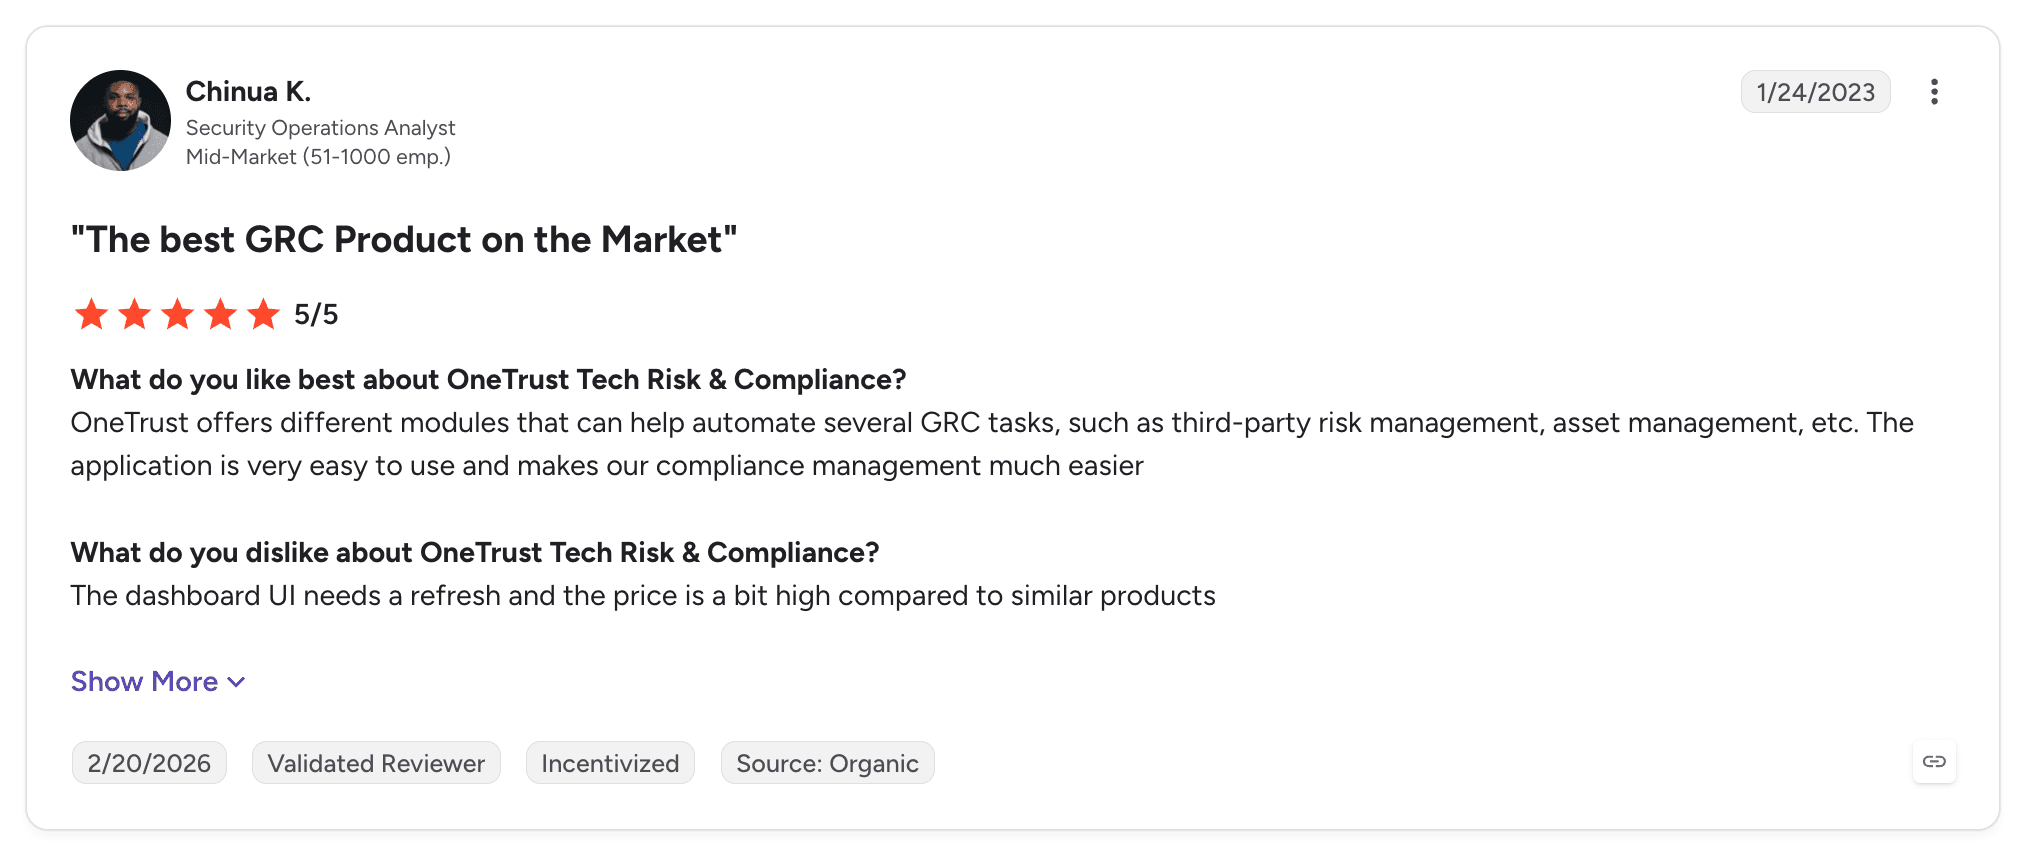
Users describe genuine consolidation. A security operations analyst calls it the best GRC product on the market, naming the modules that automate third-party risk and asset management.
Pros
Translates regulatory requirements into actionable tasks inside existing processes
Regulatory content included rather than requiring you to build the obligation library
Third-party risk and policy management in the same platform
Real-time dashboards and reporting for stakeholders
Reviewers describe strong automation across compliance workflows
Cons
Difficult setup and complex implementation are the two top-tagged weaknesses, at 6 mentions each
Learning difficulty and learning curve follow at 5 each, so the pattern is consistent
Reviewers describe reporting as lacking depth for detailed evidence requirements
Reviewers describe pricing as high and prohibitive for smaller teams
One enterprise reviewer describes scaling problems managing 27,000 domains
Inconsistent customer support is raised directly
No view of supplier contract content
Customer Reviews
OneTrust Tech Risk and Compliance holds 4.5 out of 5 across 109 G2 reviews, with 84 at five stars.
Users praise the automation and the user-friendly interface, noting the centralised dashboard and automated workflows, while flagging a steep learning curve and occasional performance issues during large-scale deployments.
The setup criticism is the most consistent signal in the data. Difficult setup, complex implementation, learning difficulty and learning curve occupy four of the five cons slots, which means the pattern is structural rather than anecdotal.
Final Verdict
OneTrust is the right choice for a large enterprise consolidating NIS2 into an existing GRC programme. The obligation mapping and regulatory content are genuine value at that scale.
Budget properly for implementation. The review data is unusually consistent that setup is complex, and reviewers describe both the time and the expertise it took.
6. ISMS.online

Overview
ISMS.online is built around the management system rather than the evidence, shipping a pre-built information security management system with documentation, risk register and policy packs.
The Assured Results Method is the guided path, taking a team through a defined sequence rather than presenting a dashboard of gaps.
It is from Alliantist, and it is the closest product here to a tool built for somebody whose job is information security management.
Ideal For
Organisations wanting a structured management system rather than evidence automation
Teams where the NIS2 gap is documentation rather than controls monitoring
Entities documenting Article 21 measures as formal policies and procedures
First-time programmes wanting a method rather than a readiness score
Top Features
Assured Results Method for a guided path through implementation
Pre-built documentation covering policies, procedures and records
Risk register with assessment, treatment and review workflows
Corrective action and incident tracking
Supplier and asset registers
Internal audit and management review scheduling
Multi-standard module support
Why It's a Strong NIS2 Option
NIS2 requires documented measures and this is the only product here built around documentation. Policies, procedures and records are the deliverable, and an evidence dashboard is not one.
The incident tracking matters for NIS2 specifically. The twenty-four, seventy-two hour and one-month reporting obligations need a process behind them, and ISMS.online has CAPA and incident modules rather than treating incidents as a control test.
Users describe auditors commenting on their organisation, which is the specific outcome the product is built to produce.
Pros
Built around the management system and its documentation
Assured Results Method gives a defined sequence rather than a gap list
Incident and corrective action tracking rather than only control testing
Supplier and asset registers included
Reviewers report auditors praising their documentation
Consistent 4.5 across both review platforms
Cons
10 integrations, far below any compliance automation platform here
Reviewers describe each regulation as a separate module with modules that do not share data
Complex navigation is the top-tagged weakness, with not intuitive behind it
Three-month implementation average, longer than the automation platforms
No view of supplier contract content
Customer Reviews
ISMS.online holds 4.5 out of 5 across 298 G2 reviews and 4.5 across 8 on Capterra. The Capterra sample is small and the scores agree.
G2's summary praises the user-friendly interface and responsive support, noting navigation can be challenging.
The most useful criticism is architectural. A reviewer rating it five out of five describes each regulation as a separate module with no data sharing, which matters if you are running NIS2 alongside ISO 27001 and GDPR.

Final Verdict
If your NIS2 problem is the documented management system, this is the right category of product. Nothing else here is built around the documentation the directive requires.
The module separation is a real constraint. NIS2 overlaps heavily with ISO 27001, and a product where those cannot share data makes you do the overlap twice.
7. Sprinto

Overview
Sprinto is a compliance automation platform aimed at fast certification, covering more than two hundred standards with hands-on support through the process.
It automates evidence collection, control monitoring and security training, with an AI feature answering inbound security questionnaires from existing evidence.
Speed is the positioning and the review base is consistent about it.
Ideal For
Fast-growing companies addressing NIS2 under time pressure
Teams without a dedicated compliance function
Organisations wanting security awareness training inside the compliance platform
Entities answering frequent inbound security questionnaires
Top Features
Automated evidence collection across 62 verified integrations
Support for 200+ standards and frameworks
Continuous control monitoring
Security awareness training automation with completion tracking
AI-assisted security questionnaire answering
Dedicated compliance expert through implementation
Why It's a Strong NIS2 Option
Security awareness training is an Article 21 expectation and Sprinto handles it inside the platform rather than requiring a separate tool.
Ease of use is tagged 384 times and customer support 319 across 1,685 reviews, which describes the product accurately as something a team without a specialist can operate.
The Capterra sample is strong and recent at 4.7 from 86 reviews with 99% positive sentiment, and the agreement between platforms is the best in this comparison.
Pros
Reviewers consistently report compliance milestones hit ahead of deadline
Ease of use and customer support are the two most-tagged strengths
Security awareness training included rather than bought separately
200+ frameworks supported
Consistent 4.7 across both review platforms
Cons
62 verified integrations, fewer than Vanta, Drata or DataGuard
Reviewers describe the platform as rigid when customising workflows
Integration issues tagged 71 times, with reviewers describing manual workarounds
Reviewers report the support experience declining after the first year
No NIS2-specific coverage and no view of contract content
Customer Reviews
Sprinto holds 4.7 out of 5 across 1,685 G2 reviews and 4.7 across 86 on Capterra, with 99% positive sentiment.
Real user reviews praise ease of use and responsive support, flagging rigidity when customising workflows.
The most useful critical review describes year two. A reviewer titles their review around the experience declining after the first year, citing slow responses and an unreliable AI assistant.

Final Verdict
Sprinto is the strongest choice for a first compliance programme under time pressure. The review base is consistent and the support model suits teams without specialists.
Ask about year two. The product is sold on getting you there, and the reviews suggest afterwards is a different conversation.
8. Secureframe

Overview
Secureframe has the strongest support reputation in this comparison. It covers the major frameworks with automated evidence collection and continuous monitoring.
Comply AI handles security questionnaires and remediation guidance, generating answers from existing evidence and suggesting fixes for failing controls.
The differentiator in its review base is the people. Customer success managers are named more often and more specifically than any feature.
Ideal For
Small and mid-sized teams with limited internal compliance capacity
Organisations valuing named human support over integration breadth
Companies wanting guided onboarding through to audit
Teams answering inbound security questionnaires regularly
Top Features
Automated evidence collection across 44 verified integrations
Continuous control monitoring with remediation guidance
Comply AI for security questionnaire answering
Dedicated customer success manager
Trust Center for publishing security posture
Policy templates mapped to framework controls
Why It's a Strong NIS2 Option
Ease of use is tagged 650 times and compliance 552 across 833 reviews, a very high density relative to the review count.
The support reputation is the real differentiator. Reviewers name their customer success manager and describe specific help, which is rarer than the marketing suggests.
The Capterra score is the highest here at 4.8 from 58 reviews with 100% positive sentiment.
Pros
Support is the most praised element across the entire review base
Ease of use tagged 650 times, the highest density here
4.8 on Capterra from 58 reviews with 100% positive sentiment
Comply AI reduces questionnaire turnaround
Reviewers describe small teams passing audits
Cons
44 verified integrations, the fewest of the automation platforms here
Integration issues tagged 184 times, the highest relative to review count
Reviewers describe control mappings needing trial and error
Reviewers describe the platform as overwhelming at first
No NIS2-specific coverage and no view of contract content
Customer Reviews
Secureframe holds 4.7 out of 5 across 833 G2 reviews and 4.8 across 58 on Capterra, with 100% positive sentiment on Capterra.
Users praise ease of use and exceptional support, noting integration issues can arise and require additional setup time.
The critical notes sit inside positive reviews. Reviewers describe a learning curve and control mappings that took iteration while still rating five out of five, which suggests the support carried them.

Final Verdict
Secureframe is the best choice for a small team wanting somebody alongside them. The support reputation is earned and clearly visible in the data.
Check your integrations first. At 44 it has the smallest estate here, and the integration-issue tag count suggests the gaps get noticed.
9. Hyperproof

Overview
Hyperproof is built for teams carrying several frameworks at once. NIS2 sits alongside ISO 27001, SOC 2 and whatever else the organisation holds.
Cross-framework mapping is the core idea. Evidence is collected once and satisfies every requirement it touches.
The product targets a dedicated compliance function rather than an engineer handling compliance part-time.
Ideal For
Compliance teams managing NIS2 alongside three or more frameworks
Organisations where the same evidence serves several regulations
Teams with a dedicated compliance function
Companies needing audit readiness tracking across a portfolio
Top Features
Control framework management across multiple standards
Cross-framework mapping so evidence satisfies overlapping requirements once
Automated evidence collection with request tracking
Audit readiness dashboards by framework
Risk register with control linkage
Issue and remediation tracking with ownership
Why It's a Strong NIS2 Option
NIS2 and ISO 27001 overlap heavily on Article 21's measures, and cross-framework mapping handles that overlap once rather than twice.
The scores are strong and consistent, at 4.5 from 223 G2 reviews and 4.8 from 116 on Capterra, with a substantial Capterra sample.
It is built for the person who owns compliance, which suits an established programme better than a founder-oriented product.
Pros
Cross-framework mapping so NIS2 evidence satisfies overlapping ISO 27001 requirements
Strong, consistent scores across both platforms
Built for a dedicated compliance function
Audit readiness tracking across a portfolio
Issue and remediation tracking with clear ownership
Cons
Reviewers cite difficulty customising reports
Reviewers describe the initial setup as unintuitive
Less suited to a single-framework programme
No view of supplier contract content
No tracking of national transpositions
Customer Reviews
Hyperproof holds 4.5 out of 5 across 223 G2 reviews and 4.8 across 116 on Capterra.
Users describe the cross-framework mapping as the specific thing that saves time, rather than a general automation claim.
Reporting and setup are the consistent criticisms, with report customisation raised repeatedly and initial configuration described as unintuitive.

Final Verdict
Hyperproof is right for a compliance team carrying NIS2 alongside other frameworks. The mapping is the value and it compounds.
It covers controls, not contracts or national law. Those are two separate gaps.
10. LogicGate Risk Cloud

Overview
LogicGate Risk Cloud is a no-code platform for building risk and compliance applications, with NIS2 as something teams build rather than a pre-configured module.
Applications are assembled from workflow components, so an organisation defines the process it wants and runs it.
The appeal is consolidation. Controls, supply chain risk and incident reporting can run as applications in one platform.
Ideal For
Organisations with an established NIS2 process they want tooling to match
Teams consolidating controls, supply chain and incident workstreams
Companies with internal capacity to build and maintain applications
Risk functions where NIS2 is one programme among several
Top Features
No-code workflow builder for configuring applications
Risk register with assessment and treatment workflows
Controls mapping across frameworks
Third-party risk management
Incident workflows with routing and escalation
Reporting dashboards built on your own data model
Why It's a Strong NIS2 Option
NIS2's incident reporting deadlines need a workflow with escalation, and LogicGate lets you build one that matches your actual process rather than a vendor's assumption.
Consolidation across the obligations is the second argument. Controls, supply chain risk and incident reporting in one platform beats three systems reconciled by hand.
The scores are solid across both platforms, at 4.6 from 191 G2 reviews and 4.7 from 65 on Capterra.
Pros
No-code builder configures to any process without development work
Consolidates controls, supply chain risk and incident reporting
Incident workflows with routing and escalation for the reporting deadlines
Reporting built on your own data model
Solid scores across both review platforms
Cons
Reviewers describe a steep learning curve on the build environment
Reviewers find the configuration interface confusing
Requires internal capacity to build and maintain applications
Nothing pre-configured for NIS2
No view of supplier contract content
Customer Reviews
LogicGate Risk Cloud holds 4.6 out of 5 across 191 G2 reviews and 4.7 across 65 on Capterra.
Users describe the flexibility as the reason they chose it, building workflows no off-the-shelf product offered.
The learning curve is the consistent criticism, with the build environment described as confusing and time to productivity longer than expected.
Final Verdict
LogicGate is right if you have a NIS2 process and want software to match it. The incident workflow flexibility is a genuine advantage given how much the thresholds vary by transposition.
It is wrong if you need to be compliant quickly. Building the applications is work and nothing is pre-configured.
What Makes a Good NIS2 Compliance Tool?
NIS2 is three problems wearing one name, and the right tool depends on which one is still open. These are the criteria that matter.
Coverage of the Obligation You Are Behind On
Article 21's risk management measures are a security control problem. Risk analysis, incident handling, business continuity, cryptography, access control and multi-factor authentication map closely onto ISO 27001, and the compliance automation platforms here handle them well.
Incident reporting is an operational workflow with hard deadlines. Twenty-four hours for an early warning, seventy-two for a notification, a month for the final report, with thresholds that differ by transposition.
Supply chain security and documented policies are legal work. Security provisions in supplier contracts, and policies that reflect what your measures actually are, are documents that need legal review rather than control testing.
Whether It Reads Supplier Contracts
Article 21 requires security in supplier and service provider relationships, and tooling consistently interprets that as vendor risk scoring rather than contract content.
The distinction is the whole thing. A vendor risk platform tells you a supplier is critical, and it does not tell you whether the agreement with them imposes security requirements, incident notification duties, audit rights or subcontracting limits.
LEGALFLY’s Multi Review is the mechanism that makes it tractable. One playbook across hundreds of supplier agreements in one pass, with every finding linked to its source clause.
How It Handles Twenty-Seven Transpositions
This is the NIS2-specific question and almost nothing on the market answers it. Member states transposed the directive on different timetables with different registration mechanisms, different incident thresholds and different penalty regimes.
A tool that treats NIS2 as one framework is tracking something that does not exist in law. What exists is the Belgian implementation, the German implementation, the Dutch implementation and twenty-four others.
Whether the Policies Get Written and Maintained
Article 21 expects documented measures, and documentation is where programmes decay. Policies adopted at implementation stop reflecting what the organisation does within months.
Template policies are not the answer on their own. They need drafting against your actual measures and updating when those measures or the underlying law change.
Discovery writes each policy against the positions your legal team has approved, and when a transposition changes, Agent Studio routes the updated policy for legal review and files the approved version. That is what keeps a policy set current instead of frozen at implementation.
What Happens to Your Data
An entity subject to NIS2 has a security function that will examine any tool touching its documents. Supplier contracts and security policies are exactly the documents that attract scrutiny.
Anonymisation before analysis is the strongest available answer. Names, roles, company details and identifiers are pseudonymised at import so identifiable data never reaches a third-party model, applied by default rather than configured per workflow.
Deployment options decide whether the review passes. SaaS, single-tenant and on-premise anonymisation deployment are three different answers, and a NIS2 entity usually needs more than the first.
To find out how LEGALFLY could work for you, schedule a call with one of our experts.
How to Choose Between the Best NIS2 Compliance Tools
Seven factors separate a purchase that closes your gap from one that duplicates your stack.
1. Name the Obligation Before You Shortlist
Be specific. Security measures, incident reporting, supply chain security and documented policies are four different problems, and most organisations have the first covered and the rest open.
Buying a second controls platform changes nothing if your controls were never the issue.
2. Ask Whether It Reads Agreements or Scores Vendors
This is the most useful question in a NIS2 software evaluation. Vendor scoring and contract reading are different capabilities, and every controls platform on this list does the first.
Test it rather than asking. Hand the vendor a supplier agreement and a list of required security provisions, and ask for output with each finding linked to its source clause.
3. Ask How It Handles the National Transpositions
Ask this directly and listen for the shape of the answer. A tool that says it supports NIS2 is supporting a directive rather than the laws you are actually subject to.
Monitoring across the jurisdictions you operate in is the only mechanism. If you operate in six member states, you need six implementations tracked, not one framework.
4. Check the Incident Workflow Against Your Thresholds
The twenty-four hour early warning is short. Ask what the detection-to-notification path looks like, who gets escalated to, and whether thresholds can differ by jurisdiction inside the same workflow.
LogicGate and ISMS.online are the two here with real incident capability. Most of the others treat an incident as a control test result.
5. Trace Remediation Past the Finding
Finding a non-compliant supplier agreement is the easy part. Ask who drafts the amendment, against which approved positions, who reviews it and where the approved version lands.
If the answer is a person and an email, you have bought a detector. Across a supplier estate that difference is the whole programme.
6. Get the Data Handling Answer Before the Security Review
Your own security function will examine this tool, which is slightly absurd and entirely predictable for a NIS2 purchase.
Ask three things. Whether documents are anonymised before any model sees them, whether that is default or configured per workflow, and what deployment options exist for entities that cannot send supplier contracts to shared infrastructure.
7. Check It Reaches Where Your Documents Live
Your supplier agreements are in SharePoint, a document management system or a contract repository. A tool that cannot read from there becomes an upload exercise.
Integration counts range from 159 down to 10 across this comparison. Ask specifically about the system holding your contracts.
Everything You Need to Know About NIS2 Compliance
Tool | Overall Rating (Based on G2 and Capterra Reviews) | Core Strength | Main Limitation | Best Fit |
LEGALFLY | 4.7 | End-to-end legal workflows on anonymised documents, covering supply chain clauses, policies and 130+ jurisdictions | Not a controls or incident reporting platform | Entities whose gap is contracts, policies or transpositions |
DataGuard | 4.6 | Names NIS2 explicitly, with named consultants reviewers praise individually | Confusing interface and rigid templates | European organisations wanting platform plus expert |
Vanta | 4.5 | Broadest framework coverage with 122 integrations and the largest review base | Pricing and contract terms draw consistent complaints | Multi-framework programmes at mid-size and above |
Drata | 4.7 | 159 integrations, the highest here, with clean audit outcomes reported | Support has shifted towards AI agents | Complex estates where integration coverage decides |
OneTrust Tech Risk & Compliance | 4.5 | Turns regulations into actionable tasks with regulatory content included | Complex setup and steep learning curve, consistently | Large enterprises with a wider GRC programme |
ISMS.online | 4.5 | Built around the management system, with real incident and CAPA tracking | 10 integrations and modules that do not share data | Organisations whose gap is documentation |
Sprinto | 4.7 | Fast implementation with hands-on support, consistent across platforms | Rigid on customisation, and support declining after year one | First programmes under time pressure |
Secureframe | 4.75 | The strongest support reputation in the category | 44 integrations, the fewest of the automation platforms | Small teams with limited capacity |
Hyperproof | 4.65 | Cross-framework mapping so NIS2 and ISO 27001 overlap once | Report customisation and unintuitive setup | Compliance teams carrying several frameworks |
LogicGate | 4.65 | No-code builder with real incident workflow flexibility | Steep learning curve, nothing pre-configured | Teams with an established process to match |
Close the Half of NIS2 Your Controls Platform Cannot Reach
Your Article 21 measures are monitored. Your supplier contracts still say nothing about security, and nobody is tracking what Belgium did differently from Germany.
LEGALFLY checks the whole estate in one pass. Multi Review applies your required security provisions across every supplier agreement, flags missing incident notification duties and unrestricted subcontracting, and Review produces the amendment language against positions your legal team has approved.
Legal Radar tracks the national transpositions individually, monitoring regulators across 130+ jurisdictions and testing each change against your own documents. Every document is anonymised before analysis begins.
ECS doubled its legal capacity with the same team. MSIG Europe took a review cycle from one day to twenty minutes. Adeera cut review time by 93%.
Book a demo and bring us a supplier agreement.
FAQs About NIS2 Compliance Software
What is NIS2 compliance software?
NIS2 compliance software helps essential and important entities meet the second Network and Information Security Directive, covering risk management measures under Article 21, supply chain security, incident reporting deadlines and management accountability. Because NIS2 is a directive rather than a regulation, it applies through twenty-seven separate national transpositions with different thresholds and deadlines. The category splits between controls and evidence platforms, enterprise GRC platforms and the legal layer handling contracts and national law.
What is the best NIS2 compliance tool in 2026?
LEGALFLY is the best NIS2 compliance tool for the legal and contractual layer, which is where most programmes have an open gap. Multi Review checks an entire supplier contract estate against your required security provisions in one pass, Review produces the amendment language, Discovery produces the policies, and Legal Radar monitors 130+ jurisdictions, which covers the national transpositions individually. Documents are anonymised before analysis begins. For Article 21's technical measures, DataGuard names NIS2 explicitly and Drata leads on integration coverage.
What should I consider when choosing the right NIS2 compliance software for me?
Start by naming which obligation is still open, because security measures, incident reporting, supply chain security and documented policies are answered by different product categories. Then ask whether the tool reads supplier contract content or only scores vendors, how it handles the twenty-seven national transpositions, and whether the incident workflow matches the thresholds in your jurisdictions. Get the data handling answer before your security review, and check the tool reaches the system where your contracts actually live.
How does LEGALFLY differ from similar alternatives?
LEGALFLY reads the supplier agreements and tracks the national laws, which no controls platform on this list attempts. Multi Review applies one playbook across hundreds of contracts at once with every finding linked to its source clause. Legal Radar monitors 130+ jurisdictions individually rather than treating NIS2 as one framework. Agent Studio then runs remediation end to end, from a detected change through drafting and legal approval to a filed document, on documents anonymised before analysis begins.
How do I get started with LEGALFLY?
Getting started begins with a scoped demo rather than a self-serve trial. Bring a supplier agreement and the security provisions you need checked, and we will run it through Multi Review on the call. Deployment covers SaaS, single-tenant and on-premise anonymisation depending on what your security function requires. Agristo had results within days of a single kickoff session.
How easy is it to switch to LEGALFLY?
Switching is straightforward because LEGALFLY sits alongside your controls platform rather than replacing it. Agreements come from SharePoint, Google Drive or NetDocuments through existing integrations, and the Word and Outlook add-ins mean legal teams work where they already work. The Playbook Builder generates a custom playbook from your own golden contracts in around two minutes, so configuring your required security provisions is not a project.
Does LEGALFLY replace my ISO 27001 or compliance automation platform?
No, and it is not meant to. Vanta, Drata, Sprinto, Secureframe and DataGuard automate control evidence collection, which LEGALFLY does not attempt. LEGALFLY covers the documents those platforms cannot read, which is the supplier agreements carrying your supply chain security obligations, the policies behind your Article 21 measures, and the national transpositions you are actually subject to. Running both is the normal pattern.
Is it safe to put supplier contracts and security policies through an AI tool when we are subject to NIS2?
It depends entirely on what the tool does with the documents, which for a NIS2 entity is the whole question. LEGALFLY anonymises documents before analysis begins, pseudonymising names, roles, company details and identifiers at import so identifiable data never reaches a third-party model, with context and structure intact. This is applied by default. LEGALFLY holds ISO 27001 and SOC 2 Type II certification, follows a framework aligned with both plus GDPR, runs annual independent penetration testing, and offers single-tenant and on-premise anonymisation deployment.
Disclaimer: This comparison reflects publicly available product information and verified user reviews as of October 2026. Ratings and review counts change over time. Product capabilities, framework coverage and integration counts should be confirmed directly with each vendor before purchase. LEGALFLY is the publisher of this comparison and is included in it.

